
More than 73,000 FortiGate VPN devices have reportedly been linked to credentials exposed in the recently disclosed FortiBleed dataset. Security teams are understandably focused on the leaked credentials. They should be equally focused on what happens next.
A compromised VPN credential doesn’t create a breach on its own. A breach happens when an attacker uses that access to reach critical systems, move laterally across the environment, and compromise the assets that matter most.
Most organizations can tell you whether a credential was exposed. Far fewer can tell you what an attacker could reach after logging in. That’s the question that matters.
Public reporting indicates attackers collected and cracked VPN authentication data at scale, then used recovered credentials to gain access to victim environments and move laterally through networks.
Nothing about this attack sequence is new.
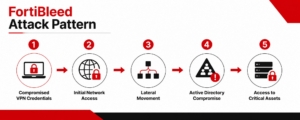
Compromised VPN Credentials → Initial Access → Lateral Movement → Active Directory Compromise → Critical Asset Exposure
Security teams have spent years strengthening perimeter defenses, deploying MFA, and improving identity controls. Yet many still struggle to answer a simple question:
If an attacker successfully authenticates today, where can they go next?
Once valid credentials are in play, the firewall is no longer the primary security boundary. Internal connectivity becomes the story.
- Can an attacker reach Active Directory?
- Can they access sensitive databases?
- Can they move into cloud environments?
- Can they pivot into operational technology networks?
- Can they reach systems that support critical business operations?
Answers to those questions determine whether an incident remains contained or turns into a headline.
If your credentials were exposed, what would you do first?
Organizations that rely on Fortinet infrastructure should assume attackers will continue targeting VPN credentials, remote access systems, and exposed management interfaces.
How quickly could your team answer these questions?
- Which FortiGate devices are internet accessible?
- Which management interfaces are exposed?
- What systems become reachable after successful authentication?
- How far could lateral movement extend?
- Which critical assets sit within reach of those attack paths?
Many organizations cannot answer those questions without days of manual investigation. Security teams already have vulnerability scanners, asset inventories, identity tools, cloud security platforms, and countless dashboards. What they often lack is a clear understanding of how those pieces connect inside the real environment.
Knowing a device is exposed is useful. Understanding the business impact if that device is compromised drives action.
Why attack path visibility matters
A FortiGate device exposed to the internet may represent little risk, or it may provide a pathway to critical business systems. Without attack path visibility, security teams are forced to guess.
Effective exposure management requires understanding:
- Whether a device is reachable from the internet
- What an attacker can access after authentication
- How lateral movement could occur across the environment
- Which critical assets are exposed
- Whether segmentation controls actually restrict attacker movement
Attackers don’t think in terms of individual vulnerabilities, credentials, or devices. They think in terms of paths. Defenders need to do the same.
How RedSeal helps
RedSeal enables organizations to understand the real-world impact of a compromise before an attacker exploits it. With RedSeal, security teams can:
- Discover FortiGate devices across hybrid environments
- Identify internet-accessible management interfaces
- Model attack paths originating from VPN entry points
- Visualize potential lateral movement to Active Directory and other high-value targets
- Measure exposure using Risk Radius to understand business impact
- Validate segmentation controls and compensating security measures
Instead of reviewing isolated alerts, teams gain a clear view of how an attacker could move through the environment and where remediation will reduce the most risk.
Immediate actions to take
Organizations concerned about potential exposure should:
- Determine whether exposed credentials associated with their organization have been identified
- Rotate VPN and administrative credentials
- Review internet accessibility of management interfaces
- Validate multi-factor authentication enforcement
- Assess attack paths originating from remote access infrastructure
- Review segmentation controls protecting critical systems
- Prioritize remediation based on business impact, not device count
One breach lesson worth remembering
FortiBleed won’t be the last credential exposure event this year. Next time it may involve a VPN credential, cloud identity, SaaS application, contractor account, or third-party platform.
Organizations that understand how an attacker could move through their environment can respond faster, prioritize more effectively, and reduce the likelihood that a compromised credential becomes a major breach.
Contact RedSeal today and learn how you can clearly see how an attacker can get in, and what they can reach once they do.

