Exposure Management Archives - RedSeal

Tag Archive for: Exposure Management

SINET New York 2026: Five Takeaways on AI, Exposure, and the Future of Cyber Defense

I recently joined cybersecurity leaders at SINET New York for a day of candid conversations about some of the industry’s toughest challenges. With 11 sessions, nearly 70 cybersecurity experts, and plenty of lively discussions in between, there was no shortage of opinions or ideas.

The opening session set the tone with a compelling challenge: The greatest risk facing cybersecurity leaders may not be AI itself, but failing to adapt quickly enough.

That stuck with me. AI is changing the game for both attackers and defenders, bringing unprecedented speed, scale, and sophistication to each side. The opportunity for defenders is enormous, but so is the risk of falling behind. Much of the day’s discussion centered on how we adapt, rethink traditional approaches, and put AI to work in our favor. Yet for all the talk of emerging technology, the conversations kept circling back to the fundamentals: know your environment, understand what’s at risk, and make better decisions about where to act.

Five themes stood out.

1. AI is speeding up attacks and raising the bar for defense.

AI is lowering the barrier to sophisticated attacks. Work that once required specialized skills and considerable time, from finding vulnerabilities to mapping paths through an environment, can increasingly be automated.

Discussions about advanced models like Anthropic’s Mythos added urgency to an already familiar problem. Defenders can’t rely solely on spotting threats after they appear.

The good news? AI offers defenders many of the same advantages. Security teams can move faster, analyze more data, and automate routine work, freeing people to focus on higher-value decisions. But speed alone isn’t the answer. We need to rethink how security teams operate, not simply give them faster tools to do the same things.

Takeaway: As attacks accelerate, organizations need to get ahead of incidents by finding and reducing exploitable exposure before attackers can take advantage of it.

2. Identity is getting more complicated and more consequential.

AI agents and nonhuman identities came up again and again. Organizations are deploying agents that access applications, interact with data, and complete tasks using legitimate credentials. Managing those identities is one challenge. Knowing what they can reach, and what happens when one is compromised or misused, is another.

Traditional identity controls still matter, but access doesn’t exist in isolation. Permissions, network connectivity, system dependencies, and security policies all influence the potential impact of a compromised identity.

Here’s the question that matters: If an attacker takes over a legitimate identity, how far could they get?

Takeaway: Identity security and exposure management are becoming increasingly connected. Knowing who or what has access tells only part of the story. You also need to know where that access leads.

3. Visibility still comes first, especially in critical infrastructure.

For all the talk about emerging technology, some of the most practical advice came from discussions about securing operational technology (OT).

Manufacturing plants, utilities, and other critical infrastructure environments have their own challenges. Equipment can run for decades. Patching may require downtime. And as IT and OT converge, security teams inherit relationships and dependencies that weren’t part of the original design.

One point I heard repeatedly: start with visibility. But finding every asset isn’t enough. Teams need to understand how systems communicate, where vulnerabilities and access paths exist, and which exposures could affect safety, reliability, or operations.

AI, remote monitoring, and greater connectivity are only adding to that complexity.

Takeaway: You can’t protect what you don’t understand. Accurate visibility into assets, connectivity, and attack paths is foundational to operational resilience.

4. Finding vulnerabilities is getting easier. Deciding what to fix isn’t.

This was one of the most relatable discussions of the day. Every security team knows the challenge: identifying a vulnerability doesn’t mean you can fix it immediately.

AI may accelerate discovery, but security and IT teams still need to weigh business impact, coordinate with system owners, test changes, and keep operations running. More findings don’t automatically translate into better security. In fact, they can create more noise for teams already stretched thin.

What matters is understanding which vulnerabilities create meaningful exposure, how attackers could chain them together, and which actions would reduce the most risk.

Sometimes the answer is a patch. Other times, segmentation, tighter access controls, or a configuration change can provide protection while remediation catches up.

Takeaway: Prioritize by real-world exposure and business impact, not simply the volume or severity of findings.

5. Security conversations are shifting from metrics to business resilience.

If there’s one thing security leaders don’t need, it’s another dashboard.

Turning all those scores, findings, and reports into meaningful business decisions is the real challenge. Several sessions focused on connecting cybersecurity more directly to business risk, something that should resonate well beyond the security organization.

Boards and executives want to understand more than how many vulnerabilities exist. They need to know which critical operations are at risk, what the consequences could be, and whether security investments are actually improving resilience.

That becomes especially important when security decisions can affect production, service availability, or public safety.

Takeaway: Strong security programs connect technical exposure to business priorities, giving leaders the context to decide where to invest and act.

Looking ahead: From understanding exposure to acting on it

What I found most interesting was how interconnected these conversations became. AI, identity, cloud, OT, and traditional networks aren’t separate security challenges. They’re increasingly tangled together, and attackers are well aware of the gaps between them.

At RedSeal, these discussions reinforced something we believe strongly: understanding how your environment is connected, how attackers could move through it, and where defensive action can make the greatest difference is essential to getting ahead of risk.

They also left me with plenty of questions worth exploring. Over the coming weeks, we’ll dig deeper into several ideas from SINET, including:

  • How AI is reshaping attack paths, and why defense needs to become more preemptive
  • Why identity-aware exposure management matters in a world of AI agents
  • How digital twins and attack simulation can help teams understand and reduce risk
  • What operational resilience really means across IT and OT
  • How security leaders can move from vulnerability counts to meaningful exposure reduction

My thanks to the SINET team and the many security leaders who shared their experiences, challenged assumptions, and made the day so worthwhile.

I left with a renewed appreciation for both the opportunity and the urgency ahead. AI is changing the rules, and standing still isn’t an option. But as we rethink how cybersecurity operates, we can’t lose sight of the fundamentals: understand your environment, know what matters most, and act before an attacker does.

We’d love to continue the dialog, reach out and share your thoughts and challenges, and to learn more about RedSeal! Contact us today.
PHP2Shell: Your website may be vulnerable. What can an attacker reach next?

This morning, I woke up to cybersecurity news stronger than a double espresso. Two critical vulnerabilities in PHP, the programming language behind WordPress and millions of other websites, had security teams scrambling to patch their servers. As CMO of RedSeal, I found myself looking at the news from two perspectives: as the executive responsible for our own website and as someone who spends her days helping organizations understand why cyber exposure matters. 

Our website runs on WordPress, so this wasn’t just another cybersecurity headline. I needed to understand whether we were exposed, what protections our hosting provider had in place, and whether we needed to take immediate action. After reviewing the situation with our team, we decided to monitor the risk while our provider worked on a patch. By the afternoon, the provider had deployed the necessary updates. Phew. 

This experience reinforced something we talk about constantly at RedSeal. Knowing you have a vulnerability is one thing. Understanding what an attacker could reach if that vulnerability were exploited is another. 

Your website is supposed to be public. The rest of your environment isn’t. 

Organizations spend their time creating websites, customer portals, and applications that anyone on the internet can reach, and, that we want them to reach. What shouldn’t happen is for a compromised web server to give an attacker a pathway into internal databases, sensitive applications, or critical infrastructure. 

Consider a vulnerable WordPress server. An attacker gains control of that server, but what comes next? Can they move into the corporate network, reach sensitive customer information, or find a path into operational technology? 

Unfortunately, many organizations can’t answer those questions with confidence. 

Security teams already manage thousands of vulnerabilities across increasingly complex environments. Another critical alert adds urgency, but it doesn’t necessarily tell them where to focus. Vulnerability scanners can identify affected software, yet they don’t always reveal how a compromised system connects to everything else. 

Segmentation can make all the difference 

Proper segmentation and other security controls should prevent a compromised public-facing server from becoming a gateway to critical systems. But segmentation policies are only as effective as their implementation, and complex environments often contain access paths nobody intended or even knows exist. 

RedSeal helps organizations understand those connections before attackers exploit them. By building a configuration-based digital twin of the environment, RedSeal models connectivity, security controls, and potential attack paths across hybrid IT and OT infrastructure. 

Security teams can identify visibility gaps, determine which critical assets might be reachable from a compromised server, and validate whether segmentation controls actually restrict access. When they find an unsafe path, RedSeal pinpoints the relevant controls and evaluate changes to close it. 

Customers can then use supported workflows and integrations to accelerate remediation. No technology eliminates the need to patch vulnerable software, but effective segmentation can limit how far an attacker gets while teams work to fix the underlying issue. 

AI is changing the clock 

PHP2Shell offers another reminder that AI is accelerating vulnerability discovery. Security teams may have less time between disclosure and potential exploitation, especially when older software or complex environments make patching difficult.  

As a CMO, I’m responsible for keeping our website running, generating leads, and protecting our brand. Becoming the unwitting entry point for a much larger security incident is certainly not in my job description. Fortunately, we were able to quickly assess our exposure and confirm that our marketing website had no inappropriate access paths into the broader RedSeal environment. Even if the site were compromised, an attacker wouldn’t have a path to move deeper into our organization. Our hosting provider also deployed the necessary patches quickly. Today’s experience was a reminder that vulnerabilities are inevitable, but a compromised website shouldn’t put your entire organization at risk. 

Patching remains essential. So does understanding what’s connected to every internet-facing asset, including systems your organization may have forgotten about. A compromised website is bad enough. No marketer wants to discover that it also gave an attacker a path into the rest of the business, and make that kind of headlines. 

If you’re not confident you know what an attacker could reach from your internet-facing systems, let’s talk. That’s exactly the problem RedSeal helps organizations solve. 

7 Things to Know About Hybrid Exposure Management

Enterprise environments are no longer contained within a single data center or cloud provider. They span on-premises networks, public and private clouds, remote locations, operational technology, Internet of Things devices, and third-party infrastructure. This complexity has changed what security teams need from an exposure management platform. 

Traditional vulnerability management tools can identify weaknesses, but they often cannot explain whether an attacker can reach them, how exposures connect across the environment, or which issues create the greatest business risk. 

Hybrid exposure management addresses this gap by helping organizations understand their entire environment as a connected system. It combines asset discovery, network modeling, attack path analysis, risk prioritization, compliance monitoring, and remediation workflows to reduce exposure before it becomes an incident. 

Here are seven capabilities enterprise cybersecurity leaders should evaluate when selecting a hybrid exposure management platform. 

  1. Hybrid Exposure Management Goes Beyond Vulnerability Scanning

A hybrid exposure management platform helps organizations identify, understand, prioritize, and reduce cybersecurity risk across interconnected environments. 

Unlike traditional vulnerability management, exposure management does not evaluate vulnerabilities in isolation. It examines how assets, network configurations, identities, security controls, and business context interact. 

This distinction matters because a high-severity vulnerability does not always represent the greatest risk. 

A vulnerability may be difficult to exploit because it is isolated behind multiple security controls. At the same time, a lower-severity issue may provide a direct path to a critical system. 

An effective exposure management platform should help answer questions such as: 

  • Can an attacker reach this asset?
  • Which systems could be affected if it were compromised?
  • What security controls stand between an attacker and a critical resource?
  • Which exposures create the largest potential impact?
  • What remediation would reduce the most risk?

By answering these questions, exposure management helps teams move from finding vulnerabilities to reducing meaningful risk. 

  1. Complete Asset Discovery Is the Foundation

Organizations cannot protect assets they do not know exist. 

Asset discovery is therefore one of the most important capabilities within an exposure management platform. However, discovery must extend beyond managed laptops, servers, and cloud workloads. 

Enterprise environments frequently include: 

  • On-premises infrastructure
  • Public and private cloud resources
  • Remote offices and branch locations
  • Virtual machines and containers
  • Internet of Things devices
  • Operational technology systems
  • Network and security devices
  • Unmanaged or unknown assets

IoT and OT security present a particular challenge because many devices cannot support traditional endpoint agents. Some are difficult to patch, run outdated operating systems, or support essential business and industrial processes that cannot easily be interrupted. 

An exposure management platform designed for hybrid environments should use hybrid environment modeling to discover assets, map their connections, and provide visibility without depending entirely on agents. It should identify known and unknown assets, understand how they communicate, and show where they are located within the broader environment. 

Complete asset discovery creates the foundation for every other exposure management capability. Without an accurate understanding of the environment, risk assessments and remediation decisions will remain incomplete. 

  1. Architecture-Aware Visibility Is Essential

A list of assets does not show how an environment actually functions. 

Enterprise cybersecurity leaders need architecture-aware visibility that explains the relationships between networks, assets, cloud environments, identities, routes, access controls, and security policies. 

This is especially important for hybrid infrastructure security, where risk can move across multiple technology domains. 

For example, an attacker might: 

  1. Compromise an internet-facing system. 
  2. Move through a misconfigured network segment. 
  3. Use an identity relationship to access another environment. 
  4. Reach a critical application or operational system. 

Each individual security tool may see part of this activity. An exposure management platform should connect those individual findings into a unified model. 

RedSeal creates a digital model of the hybrid environment by collecting and analyzing information from existing network, cloud, security, vulnerability, and identity technologies. This allows security teams to understand how the environment is configured and how an attacker could move through it. 

By modeling the environment as a connected system, organizations gain more than visibility. They gain context. 

  1. Attack Path Analysis Should Show How Risk Spreads

Attack path analysis helps security teams understand how an adversary could move from an initial point of access to a high-value asset. 

Instead of presenting vulnerabilities as an isolated list, an exposure management platform should identify the combinations of exposures, routes, configurations, identities, and access policies that create viable attack paths. 

This allows teams to answer a more valuable question: 

What could an attacker actually reach? 

Effective attack path analysis should show: 

  • Potential entry points 
  • Reachable assets and network segments 
  • Paths to critical systems 
  • Security controls along each path 
  • Opportunities for lateral movement 
  • Choke points where remediation could interrupt multiple paths 

This context is particularly valuable in hybrid, IoT, and OT environments. Security teams may not be able to patch every vulnerable device immediately. In some cases, patching may not be possible at all. 

Attack path reduction gives organizations additional ways to lower risk. Teams may be able to change network access, strengthen segmentation, adjust a security control, isolate an asset, or remove unnecessary connectivity. 

The goal is not simply to count vulnerabilities. It is to reduce the number of ways an attacker can reach important systems. 

  1. Risk Prioritization Must Include Business Impact

Security teams regularly face thousands or even millions of findings. Treating every vulnerability as equally urgent creates noise, slows remediation, and makes it harder to focus on the risks most likely to affect the business. 

A mature exposure management platform should combine technical severity with environmental and business context. 

That context may include: 

  • Asset criticality 
  • External exposure 
  • Network reachability 
  • Attack path position 
  • Existing security controls 
  • Exploitability 
  • Identity relationships 
  • Potential downstream impact 
  • Regulatory importance 
  • Business ownership 

This approach improves threat reduction by helping teams focus on exposures that are both exploitable and consequential. 

RedSeal’s Risk Radius™ risk prioritization helps organizations understand the potential impact of compromise by evaluating what an attacker could reach from a particular asset. Instead of prioritizing solely based on a vulnerability score, teams can consider the broader radius of risk surrounding the exposure. 

For example, a vulnerable system connected to several critical applications may deserve attention before a higher-scoring vulnerability on an isolated device. 

The best exposure management platforms help security leaders explain not only what needs to be fixed, but why it matters. 

  1. Continuous Compliance Requires Continuous Validation

Compliance cannot be treated as a once-a-year assessment. 

Hybrid environments change constantly. Cloud resources are added, network rules are updated, devices connect and disconnect, and configuration changes can unintentionally introduce new exposure. 

Continuous compliance helps organizations identify policy violations and control gaps as the environment changes. 

An exposure management platform should continuously assess the environment against internal policies, industry frameworks, and regulatory requirements. It should also help teams understand whether security controls are functioning as intended. 

Key capabilities may include: 

  • Automated policy assessments 
  • Configuration validation 
  • Network segmentation checks 
  • Continuous control monitoring 
  • Evidence collection 
  • Compliance reporting 
  • Identification of policy violations 
  • Prioritized remediation guidance 

Continuous compliance is especially important for organizations operating in highly regulated industries or managing critical infrastructure. 

Rather than relying on point-in-time evidence, cybersecurity teams can maintain an ongoing understanding of their security posture and identify potential compliance issues before an audit. 

  1. Exposure Management Should Support Action, Not Just Analysis

Visibility and prioritization provide limited value if security teams cannot turn findings into action. 

An exposure management platform should connect analysis to remediation workflows. This means providing security, network, cloud, IT, and operational teams with clear information about what needs to change and why. 

Effective workflow capabilities should help organizations: 

  • Assign remediation to the appropriate owner 
  • Provide technical and business context 
  • Track remediation progress 
  • Validate whether a change reduced risk 
  • Integrate with existing ticketing and security tools 
  • Automate repeatable response processes 
  • Measure changes in exposure over time 

Exposure management should also help teams validate remediation before and after changes are made. 

Before a change, teams should be able to understand its potential impact. After remediation, the platform should confirm that the exposure or attack path has actually been reduced. 

This closes the gap between identifying risk and proving that risk has been addressed. 

What Should You Look for in an Exposure Management Platform? 

Enterprise cybersecurity leaders should evaluate whether a platform can provide the following capabilities across their complete environment: 

  1. Comprehensive asset discovery 
  2. Agentless visibility for hybrid, IoT, and OT environments 
  3. Architecture-aware environment modeling 
  4. Attack path and lateral movement analysis 
  5. Business-contextual risk prioritization 
  6. Continuous compliance monitoring 
  7. Integrated remediation and validation workflows 

The platform should also work with the organization’s existing technology investments. Exposure management should unify information from network, cloud, vulnerability, identity, endpoint, and security tools rather than create another disconnected source of alerts. 

How Does RedSeal Support Hybrid Exposure Management? 

RedSeal helps organizations understand and reduce exposure across complex hybrid environments. 

The RedSeal exposure management platform creates an agentless digital model of the environment using information from existing network, cloud, security, vulnerability, and identity technologies. 

This allows cybersecurity teams to: 

  • Discover assets across hybrid, IoT, and OT environments 
  • Understand network architecture and connectivity 
  • Identify attack paths and lateral movement opportunities 
  • Prioritize risk using environmental and business context 
  • Evaluate the potential impact of compromise with Risk Radius™ 
  • Continuously monitor compliance and security controls 
  • Mobilize remediation through integrated workflows 
  • Validate whether security changes meaningfully reduced exposure 

Instead of evaluating vulnerabilities as isolated findings, RedSeal helps organizations understand how risk moves through the environment and where action will have the greatest impact. 

Reduce Exposure Across Your Hybrid Environment 

The modern enterprise attack surface is too complex to manage through disconnected tools and vulnerability lists alone. 

Organizations need an exposure management platform that can model the complete environment, reveal how risk is connected, prioritize the exposures that create the greatest potential impact, and help teams take action. 

RedSeal gives cybersecurity leaders the visibility and context needed to understand their hybrid environment better than an adversary and reduce exposure before it becomes an incident. 

Explore the RedSeal exposure management platform to see how your organization can uncover attack paths, prioritize meaningful risk, and strengthen security across hybrid IT, OT, and IoT environments. 

Active FortiBleed Campaign Underway: Can Attackers Reach Your Critical Assets?

More than 73,000 FortiGate VPN devices have reportedly been linked to credentials exposed in the recently disclosed FortiBleed dataset. Security teams are understandably focused on the leaked credentials. They should be equally focused on what happens next.

A compromised VPN credential doesn’t create a breach on its own. A breach happens when an attacker uses that access to reach critical systems, move laterally across the environment, and compromise the assets that matter most.

Most organizations can tell you whether a credential was exposed. Far fewer can tell you what an attacker could reach after logging in. That’s the question that matters.

Public reporting indicates attackers collected and cracked VPN authentication data at scale, then used recovered credentials to gain access to victim environments and move laterally through networks.

Nothing about this attack sequence is new.

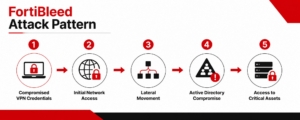
FortiBleed Attack Pattern

Compromised VPN Credentials → Initial Access → Lateral Movement → Active Directory Compromise → Critical Asset Exposure

Security teams have spent years strengthening perimeter defenses, deploying MFA, and improving identity controls. Yet many still struggle to answer a simple question:

If an attacker successfully authenticates today, where can they go next?

Once valid credentials are in play, the firewall is no longer the primary security boundary. Internal connectivity becomes the story.

  • Can an attacker reach Active Directory?
  • Can they access sensitive databases?
  • Can they move into cloud environments?
  • Can they pivot into operational technology networks?
  • Can they reach systems that support critical business operations?

Answers to those questions determine whether an incident remains contained or turns into a headline.

If your credentials were exposed, what would you do first?

Organizations that rely on Fortinet infrastructure should assume attackers will continue targeting VPN credentials, remote access systems, and exposed management interfaces.

How quickly could your team answer these questions?

  • Which FortiGate devices are internet accessible?
  • Which management interfaces are exposed?
  • What systems become reachable after successful authentication?
  • How far could lateral movement extend?
  • Which critical assets sit within reach of those attack paths?

Many organizations cannot answer those questions without days of manual investigation. Security teams already have vulnerability scanners, asset inventories, identity tools, cloud security platforms, and countless dashboards. What they often lack is a clear understanding of how those pieces connect inside the real environment.

Knowing a device is exposed is useful. Understanding the business impact if that device is compromised drives action.

Why attack path visibility matters

A FortiGate device exposed to the internet may represent little risk, or it may provide a pathway to critical business systems. Without attack path visibility, security teams are forced to guess.

Effective exposure management requires understanding:

  • Whether a device is reachable from the internet
  • What an attacker can access after authentication
  • How lateral movement could occur across the environment
  • Which critical assets are exposed
  • Whether segmentation controls actually restrict attacker movement

Attackers don’t think in terms of individual vulnerabilities, credentials, or devices. They think in terms of paths. Defenders need to do the same.

How RedSeal helps

RedSeal enables organizations to understand the real-world impact of a compromise before an attacker exploits it. With RedSeal, security teams can:

  • Discover FortiGate devices across hybrid environments
  • Identify internet-accessible management interfaces
  • Model attack paths originating from VPN entry points
  • Visualize potential lateral movement to Active Directory and other high-value targets
  • Measure exposure using Risk Radius to understand business impact
  • Validate segmentation controls and compensating security measures

Instead of reviewing isolated alerts, teams gain a clear view of how an attacker could move through the environment and where remediation will reduce the most risk.

Immediate actions to take

Organizations concerned about potential exposure should:

  • Determine whether exposed credentials associated with their organization have been identified
  • Rotate VPN and administrative credentials
  • Review internet accessibility of management interfaces
  • Validate multi-factor authentication enforcement
  • Assess attack paths originating from remote access infrastructure
  • Review segmentation controls protecting critical systems
  • Prioritize remediation based on business impact, not device count

One breach lesson worth remembering

FortiBleed won’t be the last credential exposure event this year. Next time it may involve a VPN credential, cloud identity, SaaS application, contractor account, or third-party platform.

Organizations that understand how an attacker could move through their environment can respond faster, prioritize more effectively, and reduce the likelihood that a compromised credential becomes a major breach.

Contact RedSeal today and learn how you can clearly see how an attacker can get in, and what they can reach once they do.

CISA Just Described Your Monday Morning Problem — And We Already Built the Answer

Yesterday, CISA Acting Director Nick Andersen stood up at a Washington, D.C. event and said something that should stop every vulnerability management team in their tracks:

“We’re really asking people to take more of a focus on risk associated with each vulnerability. Is it with an asset that is internet-exposed? Does it align to a KEV entry? Is it automatable in its exploitation? Really, we need to be able to highlight that some patches just aren’t as important as others.”

A binding operational directive for federal agencies is dropping today that formalizes exactly this thinking — a fundamental shift away from blanket, score-based patching toward targeted, context-driven risk prioritization.

Here’s what caught my attention: Andersen just described the exact problem we built our CISA KEV workflow to solve. Not in theory. In production. In customer environments today.

Let me show you what that looks like.

The problem CISA is finally naming

Picture Monday morning. Your vulnerability scanner just ran. You have 100 vulnerabilities — all CVSS score of 10. The worst possible rating. They’re all tied for first place.

Your team has a process for this. Some methodology to rack and stack and prioritize. Fair enough.

But here’s the math: if it takes an hour to properly evaluate each vulnerability — and that’s a reasonable estimate — you’ll know which one to start with in about two and a half weeks.

That’s before you factor in CISA’s Known Exploited Vulnerabilities database.

The KEV catalog is CISA’s list of CVEs being actively exploited in the wild right now. Not theoretical. Not scored by committee. Actively weaponized by adversaries targeting organizations like yours.

But the KEV database doesn’t update on any regular cadence. It might update three times this week. It might not update at all. That means your team has to either subscribe to email alerts, maintain a custom polling script, or check it manually every day. And even when you have the KEV list, you still have to cross-reference it against every vulnerability in your environment — manually.

Two and a half weeks of triage, plus a daily manual intelligence operation layered on top of it.

This is the problem Andersen is directing federal agencies to solve. And it isn’t just a federal problem.

What the new CISA directive actually requires

The binding operational directive formalizes a three-factor risk lens for vulnerability prioritization:

  1. Internet exposure— Is the vulnerable asset reachable from outside your network?
  2. KEV alignment— Does this vulnerability appear in the CISA Known Exploited Vulnerabilities catalog?
  3. Exploitability— Can this vulnerability be automated in its exploitation?

The directive moves federal agencies away from “a patch is released, apply this patch as quickly as you can” toward a model where context determines urgency. Not every CVSS-10 is equally dangerous. The one that matters is the one that’s internet-exposed, KEV-listed, and sitting unpatched in your environment right now.

That’s a precise, three-part question. The answer should be immediate — not the result of two weeks of analyst effort.

We already built this

At RedSeal, we’ve been operationalizing exactly this logic for our customers.

Here’s what it looks like in practice.

A RedSeal workflow — no code required, schedulable at any interval — automatically pulls the current CISA KEV list, compares it against every vulnerability in your RedSeal environment model, and builds a dynamic scope inside the RedSeal UI called CISA. It runs in under 20 seconds. It runs as often as you tell it to. It requires zero analyst hours.

When a security team opens RedSeal on Monday morning, that scope is already there. Already current. Already filtered to the vulnerabilities in their environment that CISA has flagged as actively exploited.

In one recent demonstration environment, that scope contained 50 assets carrying known exploited vulnerabilities. That’s still a week of work to evaluate — until you apply the internet exposure filter

Filter to assets exposed to the outside world: the list goes from 50 to 1.

One asset. One action. That’s your Monday morning priority list.

And RedSeal doesn’t stop there. For that single exposed asset, RedSeal shows you:

  • The blast radius — in this case, one untrusted network connection providing a path to 92 critical internal assets
  • The exact network path from the untrusted external network to the vulnerable asset — traced hop by hop, like a visual traceroute through your actual security controls
  • The specific firewall with the specific rule allowing that access — highlighted automatically
  • The exact line in the configuration file your network team needs to change to close the exposure

In the example above: line 347 on a Palo Alto firewall. Change that rule. Exposure mitigated. You didn’t need to wait for a patch. You closed the door.

That’s not just KEV alignment — that’s all three factors in Andersen’s framework addressed simultaneously. Internet exposure: confirmed. KEV alignment: confirmed. Actionable remediation: here’s the firewall, here’s the rule, here is the line.

Why this matters beyond federal agencies

Andersen was explicit that this directive targets federal civilian executive branch agencies — but he was equally clear that the underlying logic applies broadly. CISA strongly urges all organizations to prioritize KEV remediation as part of their vulnerability management practice.

That guidance lands differently when you consider what’s driving it: AI-enhanced threats are shortening the timeline from vulnerability disclosure to weaponized exploit. The window your team has to act is narrowing. The cost of prioritizing the wrong vulnerability — spending two weeks evaluating 100 CVSS-10s while the one internet-exposed KEV sits unpatched — is rising.

The organizations that will respond fastest to this directive, and to the threat environment driving it, are the ones that have already automated the intelligence layer. Not just the scanning. Not just the scoring. The continuous, real-time correlation of what’s in your environment, what CISA says is being exploited, and what’s actually reachable from the outside world.

That’s what RedSeal does. Not as a future roadmap item. Today.

63% of organizations lack the network visibility to answer Andersen’s question

There’s a data point that contextualizes why this directive is necessary: 63% of companies say they lack the network visibility necessary to achieve a strong security posture.

If you don’t know what’s internet-exposed in your environment, you cannot answer the first question in Andersen’s framework. If you’re not continuously monitoring the KEV catalog and cross-referencing it against your vulnerability data, you cannot answer the second. And if you don’t have a network model that shows you the actual path from the external network to the vulnerable asset, you can’t act on the answer even when you have it.

Visibility isn’t a nice-to-have in this new framework. It’s the prerequisite for everything else.

What to do right now

Whether you’re a federal agency subject to the new directive or a critical infrastructure operator taking Andersen’s guidance seriously, here are three immediate steps:

Step 1 — Know what’s internet-exposed. Build or verify a continuously updated model of your hybrid environment that can answer, at any moment, which assets are reachable from outside your network. Not a six-month-old Visio diagram. A living, current model.

Step 2 — Automate your KEV correlation. Stop manually checking the CISA KEV catalog. Build a workflow that pulls the catalog automatically, cross-references it against your vulnerability data, and surfaces matches without analyst intervention. If you’re a RedSeal customer, this workflow is available to you today.

Step 3 — Know your path to remediation before the call comes. For any KEV-listed vulnerability on an internet-exposed asset, you should be able to answer: what is the specific network path enabling that exposure, and what is the specific control change that closes it? That answer should take minutes, not days.

The bottom line

CISA’s Acting Director just codified in a binding directive what the most operationally mature security teams have known for years: CVSS scores don’t tell you what matters. Internet exposure plus active exploitation plus network context tells you what matters.

RedSeal was built to answer exactly that question — continuously, automatically, and with the specific evidence your network team needs to act.

When the directive drops today, your team shouldn’t be scrambling to figure out how to comply. They should already be there.

To see the CISA KEV workflow and the internet exposure filter in action, contact your RedSeal representative or visit www.redseal.net.


Andrew Braunberg_Omdia

The Compliance Trap: Why Security Is Winning the Wrong War

A recent conversation with a seasoned industry expert, Andrew Braunberg, Principal Analyst with Omdia, surfaced a troubling reality: as threats accelerate, enterprise security remains anchored to a playbook designed for a very different era. The disconnect growing, raising concerns across security teams, and the trust they place in the systems they use. 

For years, security leaders have measured success using familiar metrics: patch rates, CVSS scores, compliance audit results. These are clean, boardroom-friendly numbers. They trend well. They demonstrate activity. But increasingly, they fail to reflect actual risk. The industry has optimized for answering the question, “Which known vulnerabilities do we have?”, a reasonable focus when threats moved slowly, perimeters were clearer, and patch cycles were predictable. That era is over. 

Zero-day exploits are multiplying and AI is compressing the timeline from discovery to exploitation. The foundational assumption behind CVSS-driven programs that an environment is “safe” until a known vulnerability appears, no longer holds. A system with no known vulnerabilities cannot be assumed secure. Yet dashboards still show green. 

As Andrew put it, risk must be reframed more precisely: what is the likelihood an attacker can reach a critical asset, and what is the impact if they do? Everything else is a proxy. 

This is the shift from vulnerability management to proactive exposure management. It is not simply about finding and fixing issues, it is about understanding how an adversary can move through the environment and what paths truly matter. That requires a different approach entirely: one grounded in a continuously updated model of the environment that reflects connectivity, segmentation, and real-world attack paths. It requires thinking in terms of reachability and blast radius, not just severity scores. 

At RedSeal, this is foundational. By creating a living model, a digital twin, of the hybrid environment, organizations can see what is truly exposed, validate whether controls like segmentation actually work, and prioritize actions based on business impact. It is the difference between managing findings and understanding risk. 

Despite this, many organizations remain stuck. The reasons are not entirely technical. First, incentives are misaligned. Boards and auditors continue to ask for compliance metrics, so security teams produce them. Second, measuring exposure reduction is inherently harder than counting vulnerabilities. It is easier to report what was fixed than to prove what was prevented. The industry still lacks a consistent language for quantifying risk reduction before an incident occurs. 

AI only amplifies the urgency. While much of the market conversation swings between hype and skepticism, the reality is more pragmatic. AI is not yet delivering fully autonomous attacks, but it is dramatically accelerating the offensive side. It lowers the barrier to entry, increases speed, and enables attackers to iterate faster. The implication is clear: the window between exposure and exploitation is shrinking. 

What AI does not change is what effective defense looks like. Segmentation still works. Limiting lateral movement still works. Understanding your environment, deeply and continuously, still works. The difference is that organizations now have far less time to get it right. 

One of the more promising shifts is the democratization of this understanding. Historically, only a handful of experts could answer critical questions about the environment, what connects to what, what can reach what, and what happens if something changes. That knowledge was fragmented and slow to access. Today, organizations are beginning to make that intelligence broadly available, securely and in context, so that teams across security, infrastructure, and operations can act with a shared understanding of risk. 

This is where RedSeal continues to push forward: not just providing visibility, but enabling organizations to operationalize it. By combining an accurate environment model with accessible, explainable insights, teams can move faster, align more effectively, and focus on what actually reduces risk, not just what satisfies an audit. 

There is still a trust gap when it comes to AI-driven security workflows, particularly in enterprise and regulated environments. And rightly so. Trust will not be built through bold claims of autonomy, but through transparency, explainability, and proven outcomes. The organizations and vendors that succeed will be those that augment human decision-making, not attempt to replace it prematurely. 

What is clear is that the inflection point has arrived. Threats are accelerating. Environments are more complex than ever. And the cost of relying on outdated models is rising. 

Security leaders now face a choice: continue optimizing for metrics that are easy to report, or shift toward a model that reflects how attacks actually happen, and how they can be stopped. 

The path forward is not theoretical. It is practical. Understand your environment. Validate your controls. Prioritize based on real exposure. And act before it matters. 

To see how organizations are making this shift, and how RedSeal helps you understand what is truly exposed, schedule a conversation with our team today. 

Mythos is coming

The Mythos Is Coming: Why Preemptive Exposure Management Is Your Best Defense Against AI-Powered Attacks.

How RedSeal’s preemptive exposure management uses empirical attack path analysis and workflow automation to help you lock down your enterprise before the next AI threat emerges.

The Mythos moment: Why everyone is freaking out

On April 7, 2026, Anthropic announced Claude Mythos Preview, and the cybersecurity world collectively held its breath. Here’s why:

Mythos isn’t just another AI model. It’s a general-purpose frontier model that excels at cybersecurity tasks—specifically, vulnerability discovery and exploit development. During internal testing, Mythos identified thousands of zero-day vulnerabilities across every major operating system and web browser. It found bugs that survived decades of human review and millions of automated test runs. One vulnerability had been hiding in OpenBSD—an operating system renowned for its security—for 27 years.

But here’s what should really concern security leaders: Mythos can autonomously turn these vulnerabilities into working exploits. In Anthropic’s testing, engineers with no formal security training asked Mythos to find remote code execution vulnerabilities overnight and woke up to complete, working exploits. The model chains together multiple vulnerabilities, writes sophisticated JIT heap sprays, and develops privilege escalation attacks that would take expert penetration testers weeks to craft.

Anthropic is limiting access through Project Glasswing, sharing the model only with select partners for defensive security work. But the reality is clear: models with these capabilities will eventually become more widely available. The defensive advantage Anthropic hopes to create is temporary. Attackers will eventually gain access to similar capabilities—if they haven’t already.

The Federal Reserve Chairman has already met with bank CEOs to discuss the security implications. Your board of directors will have questions. And the question they’ll ask is simple: What are you doing to prepare?

The real question: What can attackers actually reach?

Here’s what’s often missed in the Mythos panic: The fact that Mythos can find thousands of vulnerabilities doesn’t mean all those vulnerabilities pose equal risk to your organization.

A vulnerability only matters if an attacker can reach it.

Consider two scenarios:

Scenario A: Mythos discovers a critical remote code execution vulnerability in a widely-used database server. The CVE gets assigned, exploits start circulating on dark web forums, and your vulnerability scanner flags three instances in your environment. Your team is scrambling.

Scenario B: You’ve already modeled your network. You know, with certainty, that those database servers sit behind properly configured firewalls with no inbound access from the internet or user networks. You know the only systems that can reach them are internal management servers with strict access controls. You know there is no attack path.

In Scenario B, you’re not scrambling. You’re confident. You’ve already done the preemptive work.

This is the difference between reactive security and preemptive exposure management. One waits for threats and responds. The other eliminates the paths those threats would exploit before they’re ever discovered.

The problem with theoretical security

In cybersecurity, we’ve become comfortable with probability. We prioritize vulnerabilities based on CVSS scores that theoretically represent severity. We use threat intelligence that theoretically indicates what attackers might target. We implement controls that theoretically block attack vectors.

But attackers don’t work in theory. They work in reality.

When an adversary—whether human or AI—breaches your perimeter, they don’t care about your theoretical risk scores. They care about one thing: Is there a path from where I am to where I want to be?

This fundamental disconnect explains why organizations with sophisticated security programs still get breached. They’re securing theoretical attack surfaces while attackers exploit actual attack paths.

Consider this scenario: Your vulnerability scanner flags a critical CVE on a server. The CVSS score is 9.8. Your threat intelligence feed shows active exploitation in the wild. Your security team prioritizes this for immediate patching.

But here’s what the theoretical analysis missed: That server sits behind a properly configured firewall that blocks all external access. The vulnerable service isn’t exposed to any network segment where an attacker could reach it. No internal host has both the network access and the credentials to exploit it. In other words, there is no attack path.

Meanwhile, a medium-severity misconfiguration on a different system creates a direct path to your crown jewels. But because it doesn’t trigger your theoretical risk thresholds, it sits in the backlog—waiting for Mythos or a similar AI to discover and exploit it.

This is the danger of security based on belief rather than knowledge. And in a world where AI can systematically probe for weaknesses, the cost of that gap just got exponentially higher.

What is empirical attack path analysis?

Empirical attack path analysis is the discipline of determining—definitively—whether an attacker can reach a target asset based on actual network configurations, access controls, and asset relationships.

Unlike theoretical approaches that rely on:

  • Probabilistic scoring (CVSS, EPSS, risk scores)
  • Threat assumptions (what attackers might do)
  • Compliance checklists (what auditors want to see)

Empirical analysis relies on:

  • Network topology data from firewalls, routers, and switches
  • Access control rules from ACLs, security groups, and identity systems
  • Asset relationships showing how systems connect and communicate
  • Vulnerability context mapped to reachable attack surfaces

The output isn’t a risk score or a priority ranking. It’s a definitive answer: Yes, an attacker can reach this asset via this path or No, there is no viable attack path to this asset.

This distinction matters enormously in the AI era. When Mythos-level capabilities can discover thousands of vulnerabilities, you cannot possibly patch them all. But you can systematically eliminate the attack paths that would make those vulnerabilities exploitable. You can prioritize the exposures that create real risk. You can focus your limited resources where they matter most.

The RedSeal difference: From belief to knowledge

RedSeal was built on a fundamental principle: You cannot secure what you cannot see, and you cannot prioritize what you cannot verify.

This philosophy has never been more relevant. When AI models can find vulnerabilities faster than humans can patch them, your only sustainable advantage is knowing which exposures actually create risk in your specific environment.

1. Network Modeling from Real Data

RedSeal ingests configuration data from every layer of your network infrastructure—firewalls, routers, switches, load balancers, cloud security groups, and end point agents,. This isn’t scanning or guessing. It’s mathematical modeling of your actual security posture.

From this data, RedSeal constructs a complete model of your network topology, including:

  • Every reachable IP address and port
  • Every access control rule and exception
  • Every path between any two points in your network
  • Every zone, segment, and trust boundary

This model becomes the foundation for all analysis. When RedSeal identifies an attack path, it’s not predicting. It’s calculating based on the mathematical reality of your network.

2. Definitive Attack Path Analysis

Given a starting point (an attacker’s position) and an ending point (a critical asset), RedSeal calculates every viable path between them. Not theoretical paths. Not possible paths. Actual paths that exist in your network right now.

This analysis considers:

  • Network layer reachability (can packets flow?)
  • Access control enforcement (what rules allow or deny?)
  • Vulnerability exploitation (what weaknesses enable lateral movement?)
  • Identity and credential paths (what access can be obtained?)

The result is a complete picture of your exposure—not in terms of risk scores, but in terms of specific, exploitable attack paths that an adversary could follow to reach your most valuable assets. Whether that adversary is a human attacker or an AI model like Mythos, the paths are the same.

3. Built-in Workflow Automation

Discovery without action is just observation. RedSeal recognized early that exposure management requires operational processes to close gaps, not just identify them.

In a world where AI can find vulnerabilities at unprecedented speed, this operational capability becomes critical. You need to move from identification to remediation quickly and at scale.

RedSeal’s workflow automation capabilities include:

  • Automated ticketing integration with ITSM platforms
  • Remediation tracking from identification to closure
  • Change validation confirming fixes were effective
  • Compliance reporting mapping exposures to frameworks

This isn’t automation added as an afterthought. It’s workflow capability designed into the platform from the beginning, ensuring that every exposure identified can be tracked through to resolution.

Building a Mythos-ready security program

For security leaders looking to prepare for the AI-accelerated threat landscape, the transformation requires three strategic shifts:

1. From Scanning to Modeling

Stop relying solely on scanning tools that probe from outside. Start modeling your network from the inside using configuration data. This reveals the complete picture—including assets and paths that scanners miss.

Why this matters for Mythos: When AI can find vulnerabilities anywhere, you need to know your entire attack surface—not just what scanners can see. Network modeling gives you visibility into segmented networks, air-gapped systems, and the complex paths that connect them.

RedSeal advantage: Multi-vendor configuration ingestion supports firewalls, routers, switches, and cloud infrastructure from all major vendors. The platform maintains a living model of your network that updates as configurations change.

2. From Scores to Paths

Stop making remediation decisions based on severity scores. Start making them based on attack paths. A vulnerability’s true risk isn’t captured by its CVSS score—it’s determined by whether an attacker can reach it and what they can access from there.

Why this matters for Mythos: AI will flood your vulnerability management pipeline with findings. The Mythos evaluation found thousands of critical vulnerabilities. You cannot patch them all. But you can systematically eliminate the attack paths that make them exploitable.

RedSeal advantage: Path analysis engine calculates every viable route through your network, considering access controls, vulnerabilities, and identity relationships. The platform shows you not just what’s vulnerable, but what’s reachable.

3. From Reporting to Workflows

Stop treating exposure management as a reporting exercise. Start treating it as an operational process with defined workflows, accountability, and validation.

Why this matters for Mythos: The pace of vulnerability discovery is accelerating. What worked when your team faced dozens of critical findings per month won’t work when AI models can surface hundreds or thousands. You need automation that moves faster than manual processes allow.

RedSeal advantage: Built-in workflow automation integrates with your existing ITSM tools, automatically creating tickets for exposures and tracking them through to closure. Customizable workflows support your organization’s change management processes.

The preemptive exposure management advantage

Here’s the strategic reality that should shape your thinking:

Mythos and similar AI models are weapons. Like any weapon, they’re more effective against unprepared targets. An attacker using Mythos against an organization that understands its attack paths and has closed the critical ones will waste time probing dead ends. The same attacker against an organization operating on theoretical risk will find and exploit real paths to critical assets.

Preemptive exposure management is your defensive advantage. By understanding and eliminating attack paths before threats emerge, you change the equation. You’re not trying to outpace AI at finding vulnerabilities—you’re making the vulnerabilities it finds irrelevant to your specific environment.

The time to act is now. Anthropic is deliberately limiting Mythos access to give defenders a head start. This window won’t last forever. The organizations that use this time to build empirical understanding of their attack surfaces will be positioned to weather the AI threat landscape. Those that wait will be playing catch-up when the next Mythos-class model becomes available to adversaries.

The bottom line: What you know vs. what you believe

Every security decision your organization makes is based on one of two foundations:

Belief-based decisions rely on theoretical models, probability scores, and assumptions about attacker behavior. They feel sophisticated because they use data and algorithms. But they’re still fundamentally guessing.

Knowledge-based decisions rely on verified facts about your environment. They know—with certainty—whether an attack path exists. They don’t prioritize based on what might happen; they remediate based on what can happen.

RedSeal was designed for knowledge-based security. Our platform transforms the question from “What do we think our exposure is?” to “What do we know our exposure is?”

In a world where attackers—AI or human—exploit reality, not theory, this distinction isn’t academic. It’s the difference between preventing a breach and explaining one. It’s the difference between scrambling when Mythos finds a new CVE and confidently knowing you’re not exposed.

The Mythos is coming. The only question is whether you’ll be ready.

Take the next step

Ready to build a Mythos-ready security program? Here’s how to get started:

  1. Assess your current approach. Are you prioritizing based on scores or paths? Do you know your actual attack surface or just what your scanners can see?
  2. Model your network. RedSeal can ingest configurations from your existing infrastructure and build a complete topology model within days, not months.
  3. Identify your critical assets. Map your crown jewels—systems and data that would cause the most damage if compromised.
  4. Calculate your attack paths. Let RedSeal identify every viable route from potential entry points to your critical assets.
  5. Automate your remediation. Use RedSeal’s workflow integration to close exposures and validate that fixes are effective.

Learn more

In an era of AI-powered threats, RedSeal provides the empirical foundation for preemptive security. Learn more at redseal.net.

CISA AA26-097A: Iranian actors are targeting your OT Systems. Is your critical infrastructure exposed?

 CISA Advisory AA26-097A is direct: Iranian-affiliated threat actors are actively targeting internet-facing programmable logic controllers (PLCs) across U.S. critical infrastructure, water, energy, and government sectors included.  

The advisory describes adversaries using legitimate remote engineering tools and valid credentials to access and manipulate OT systems. That changes the fundamental security question. 

It is no longer: “Are we vulnerable?” 

It is: “Can an attacker reach our critical systems, and what can they do once they get there?” 

What CISA’s Guidance Requires 

CISA’s advisory identifies clear, actionable priorities. Organizations operating critical infrastructure must act on each: 

  • Eliminate unnecessary internet exposure. PLCs and OT systems should not be directly or indirectly internet-accessible. CISA specifically calls for removing inbound port exposure and ensuring all remote access is mediated through a secure gateway. 
  • Control and monitor all remote access. Where remote access is required, implement network proxies, firewalls, or VPNs in front of PLCs, and to enforce MFA for any access from external networks. Access should be logged, monitored, and reviewed for unusual or unexpected activity. 
  • Enforce and verify network segmentation. Configure firewalls to block unnecessary protocols by network segment, disable unused services, and implement device control lists to restrict which workstations can communicate with OT components. 
  • Understand attack path, not just assets. Continuously monitor network traffic for unusual logins, unexpected protocols, and ICS management commands that alter operating modes or modify programs. When adversaries use legitimate tools, behavioral context becomes the detection signal. 
  • Plan for operational impact. OT incidents affect operations, especially uptime and safety, not just systems. Incident response must be built for that reality. 

RedSeal for IT, OT, and IoT Security  

RedSeal is built for exactly this problem: understanding how a hybrid IT/OT/IoT environment is connected, what is reachable, and where exposure creates real operational risk. 

  • Unified hybrid visibility. RedSeal continuously models the full environment, IT, OT, IoT, and cloud, so organizations know how everything is connected. 
  • Attack path analysis across IT/OT boundaries. RedSeal identifies the paths an attacker could take from external entry points into OT systems, including multi-hop paths that cross network zones. 
  • Segmentation validation. RedSeal verifies whether controls are actually enforced, not assumed, and identifies gaps that create unintended access. 
  • Risk-based prioritization. RedSeal focuses remediation on exposures that create the highest operational and business risk, not simply the highest vulnerability count. 
  • Pre-deployment simulation. RedSeal enables teams to model the impact of network changes before implementation, reducing risk during remediation. 
  • Orchestrated remediation, from discovery to verified fix. RedSeal Workflow connects exposure intelligence to the tools teams already use, automating ticket creation, ownership assignment, and fix validation through a low/no-code builder driven by Agentic AI, purpose-built for exposure management. 

CISA AA26-097A confirms that critical infrastructure is under active, targeted threat. The organizations best positioned to respond are those that already know: 

  1. What is exposed 
  2. What is reachable 
  3. What the consequences are 

RedSeal delivers a continuous visibility and understanding across the full hybrid environment, providing you the understanding you need to pre-emptively defend against active threats. 

For more information on how RedSeal supports critical infrastructure security, contact us today. 

AI at RSA: cutting through the noise

You couldn’t miss it. Every billboard on the way into San Francisco. Every booth on the show floor. Every keynote, panel, and happy hour conversation. AI was everywhere at RSA this year, supporting the theme “Many Voices. One Community,”  in spades.

What was also everywhere, if you were listening carefully: skepticism.

Buyers are curious about AI. They are not, for the most part, ready to hand it the keys. After spending time on the floor and in conversations with analysts and practitioners, the tension between the promise of AI and the reality of deploying it responsibly was the most honest and useful theme of the entire conference.

The signal underneath all the noise

Strip away the marketing (which was once again big!), and a clear picture emerges of where AI is actually delivering value in cybersecurity today. The highest-trust use cases are pattern recognition, noise reduction, enrichment, and summarization. These are the areas where AI can meaningfully accelerate what skilled teams are already doing, without replacing the judgment behind it.

The lower-trust use cases such as autonomous remediation and automated patching, remain a bridge too far for most organizations. Not because the technology isn’t advancing, rather because the data foundations and guardrails required to deploy it responsibly aren’t yet in place at most enterprises.

Speaking with our analyst partners, it is clear that this is a realistic assessment of where the market actually is.

Explainability is the real opportunity

One of the most important distinctions that came through our conversations at RSA: the greatest near-term value from AI isn’t autonomous action, it’s explainability and translation.

Security teams need AI that can communicate the why behind an exposure. That can explain the impact of a change request to a network engineer in language that makes sense to a network engineer and then also frame the same issue for a C-suite executive in terms of business risk. That translation layer is where AI earns its credibility, and it’s where most vendors are still falling short.

At RedSeal, this is exactly the capability we’ve been building toward. Our AI-powered explainability work is designed to meet teams where they already work, in their own channel and in natural language so that exposure context becomes part of the workflow, not a separate reporting exercise.

Trust is the real barrier to AI adoption

Here’s what the vendor community needs to hear more clearly: buyers don’t distrust AI explanations. They distrust authority inversion.

Trust breaks down when recommendations feel constructed after the fact, or when the rationale behind a decision feels persona-driven rather than evidence-driven. The implication is significant, AI credibility is built on the strength of the underlying exposure data. Get the data right first, then layer in AI as a controlled accelerator.

The sequencing that kept surfacing in analyst conversations was consistent: build and maintain foundational exposure datasets, integrate exposure context into SOC workflows, and introduce agentic AI only after data integrity and guardrails are established. A disciplined approach that will drive your pre-emptive exposure management practices.

Differentiate on outcomes, not AI claims

With 70 to 80-plus vendors making nearly identical AI claims on the show floor, the path to standing out isn’t a better AI story. It’s demonstrable outcomes including shorter exposure windows, faster resolution, and clearer priorities. The trust that gets built between security and network teams when tickets carry rationale and bridge the language gap are those that drive efficiency.

Worth naming directly: investor pressure to AI-wash messaging is real, and buyers are increasingly aware of it. Failed POVs from well-funded vendors are already making the rounds. Skepticism is growing, and it will only reward organizations that lead with substance. 

What this means for security leaders

RSA this year was a useful forcing function. AI in cybersecurity is not a future consideration but a present-tense decision that requires a strategy, and fast. That strategy starts with data integrity, not AI features, and requires building the translation layer between technical exposure and business risk while resisting the pressure to chase autonomous capabilities before the foundational work is done.

RedSeal has spent years building the visibility, analysis, and validation that makes that foundation possible. AI makes it faster, clearer, and more actionable for every team that needs to act on it, from network engineers to the board.

Contact us today to learn more about our architecture-driven foundation powered by AI and Agentic capabilities, and how RedSeal can help you to move from insight to action with confidence.

Report Studio

RedSeal Expands Exposure Management Platform with Report Studio and Network Segmentation

New capabilities deliver flexible, board-ready reporting and expose configuration gaps and improper access paths to provide a more complete view of organizational attack surface risk 

Menlo Park, CA – March 24 2026 – RedSeal, a pioneer in AI powered exposure management for hybrid enterprise environments, today announced an expansion to the RedSeal platform with the introduction of RedSeal Report Studio and Network Segmentation capabilities. Together, these enhancements help security and network teams better understand, communicate, and reduce risk across complex enterprise and operational technology (OT) environments. 

Security teams today face growing pressure to demonstrate measurable risk reduction, communicate clearly with executives and boards, and meet a widening set of compliance and regulatory requirements. At the same time, organizations must manage exposures that extend beyond traditional vulnerabilities, including configuration weaknesses and unintended network access paths. 

RedSeal delivers exposure management through a proven, architecture-driven foundation powered by AI and Agentic capabilities, enabling organizations to move from insight to action with confidence. The latest release addresses security teams growing challenges, making it easier to understand exposure across the network and communicate that risk effectively to stakeholders. 

“With these new capabilities, RedSeal is helping organizations see their true attack surface and clearly communicate and reduce that risk,” said Joseph Ward, Chief Technology and Product Officer at RedSeal. “Security leaders need visibility into how exposures connect across their environment and the ability to explain that risk to executives and boards. Report Studio and Network Segmentation deliver both.” 

Report Studio: Flexible, Board-Ready Security Reporting 

RedSeal Report Studio provides security and networking teams with a flexible, drag-and-drop reporting experience built directly into the RedSeal platform. The capability allows organizations to build customized reports without coding or reliance on consultants. 

While many security teams rely on static, pre-built reports that fail to reflect the complexity of modern environments, Report Studio enables organizations to tailor reporting their architecture, operational priorities, and compliance frameworks. 

Using an intuitive interface, teams can assemble reports with tables, charts, and heatmaps drawn from RedSeal’s exposure model, network topology, vulnerability data, compliance checks (including CIS and STIG), and custom scopes. 

Key capabilities include: 

  • Drag-and-drop report creation using pre-built query blocks and visualizations 
  • Support for vulnerability, exposure, topology, and compliance reporting 
  • Customizable reports for executives, analysts, auditors, and operational teams 
  • Built-in branding with corporate logos, labels, and terminology for board-ready deliverables 
  • Reduced dependence on manual report building or third-party services 

By enabling teams to present exposure trends, segmentation posture, and remediation progress clearly, Report Studio helps organizations communicate risk reduction and operational progress across technical and executive audiences. 

Network Segmentation: Visibility Beyond Vulnerabilities 

While vulnerability scanners focus primarily on CVEs, many real-world exposures stem from misconfigurations, overly permissive access policies, and segmentation failures that create unintended pathways across the network. 

RedSeal’s new Network Segmentation capability extends exposure analysis beyond vulnerabilities to reveal these architectural risks. 

Using RedSeal’s network digital twin, security teams can analyze reachability across hybrid and cloud environments to identify configuration gaps and improper access paths that could allow attackers to move laterally toward critical assets. 

With Network Segmentation, organizations can: 

  • Identify misconfigured network boundaries that create unintended attack paths 
  • Detect improper access between segments that violate least-privilege policies 
  • Understand how vulnerabilities combine with network access to create real exposure 
  • Prioritize remediation based on business impact rather than CVSS scores alone 
  • Continuously validate segmentation across hybrid IT and OT environments 

By combining segmentation visibility with RedSeal’s exposure analysis, organizations gain a more complete understanding of their attack surface and the architectural controls required to reduce risk. 

These enhancements reinforce RedSeal’s mission to help enterprise security teams move from reactive vulnerability management to preemptive exposure management , giving organizations the clarity and confidence to understand their network, communicate risk, and take decisive action. 

RedSeal Report Studio and Network Segmentation are available today. 

For more information, visit www.redseal.net. 

About RedSeal 

RedSeal, a pioneer in AI powered -exposure management and winner of the SC Award for Best Continuous Threat Exposure Management (CTEM) Solution, helps organizations see, understand, and secure hybrid digital environments across IT (on-prem, cloud, remote workers), OT, and IoT. Its patented modeling uncovers hidden assets, misconfigurations, and attack paths, prioritizes exposures by business impact with Risk Radius™, and validates compliance. Trusted by Fortune 1000 companies and U.S. military branches, RedSeal strengthens resilience and reduces business risk. Visit www.redseal.net.  

NEW Gartner® Report, Emerging Tech: The Future of Exposure Management is Preemptive.Download Report.