Advisory Notice: MOVEit Transfer Critical Vulnerability - RedSeal
RedSeal
  • Platform
    • RedSeal Platform
    • Capabilities
      • Hybrid Environment Modeling
      • Attack Path Analysis
        addyi
      • Risk Prioritization
      • Continuous Compliance
    • Integrations
    • CTEM
  • Services
    • CTEM
    • Professional Services
    • Customer Support
    • RedSeal University
  • Solutions
    • Business Use Cases
      • Breach Impact Reduction
      • Mergers & Acquisitions
      • Cyber Insurance Optimization
    • Industries
    • CTEM
  • Partners
    • RedSeal Partners
    • Partner Portal
  • Company
    • About RedSeal
    • Leadership
    • Careers
  • Resources
    • Blog
    • Events
    • Resource Center
  • Contact Us
  • GET A DEMO
  • Click to open the search input field Click to open the search input field Search
  • Menu Menu

Advisory Notice: MOVEit Transfer Critical Vulnerability

2023-06-21
/  byRedSeal

CVE: CVE-2023-35708

Description:

Progress has discovered a vulnerability in MOVEit Transfer that could lead to escalated privileges and potential unauthorized access to the environment. If you are a MOVEit Transfer customer, it is extremely important that you take immediate action as noted below in order to help protect your MOVEit Transfer environment. In Progress MOVEit Transfer versions released before 2021.0.8 (13.0.8), 2021.1.6 (13.1.6), 2022.0.6 (14.0.6), 2022.1.7 (14.1.7), 2023.0.3 (15.0.3), a SQL injection vulnerability has been identified in the MOVEit Transfer web application that could allow an un-authenticated attacker to gain unauthorized access to the MOVEit Transfer database. An attacker could submit a crafted payload to a MOVEit Transfer application endpoint which could result in modification and disclosure of MOVEit database content.

Recommended Mitigation Steps:
  1. Disable all HTTP and HTTPs traffic to your MOVEit Transfer environment. More specifically:
      • Modify firewall rules to deny HTTP and HTTPs traffic to MOVEit Transfer on ports 80 and 443.
      • It is important to note that until HTTP and HTTPS traffic is enabled again:
        • Users will not be able to log on to the MOVEit Transfer web UI.
        • MOVEit Automation tasks that use the native MOVEit Transfer host will not work.
        • REST, Java and .NET APIs will not work.
        • MOVEit Transfer add-in for Outlook will not work.
      • SFTP and FTP/s protocols will continue to work as normal.
  2. As a workaround, administrators will still be able to access MOVEit Transfer by using a remote desktop to access the Windows machine and then accessing https://localhost/. 
 
For more information on localhost connections, please refer to MOVEit Transfer Help: https://docs.progress.com/bundle/moveit-transfer-web-admin-help-2023/page/Security-Policies-Remote-Access_2.html
  3. Apply the Patch
    As patches for supported MOVEit Transfer versions become available, links will be provided below. Supported versions are listed at the following link: https://community.progress.com/s/products/moveit/product-lifecycle. Please note, the license file can remain the same when staying on a major release to apply the patch.
  4. Enable all HTTP and HTTPs traffic to your MOVEit Transfer environment
  5. Please bookmark the Progress Security Page and refer to it to ensure you have all of the latest updates.
How Can RedSeal Help?
  • By bringing Host Data into your RedSeal instance, we can identify hosts with the targeted CVE in both the “Endpoint Data” tab, as well as the “Vulnerabilities” tab.
  • First be sure to update your CVE definitions on your endpoint scanning system and run a data collection in RedSeal.
  • If the vulnerability does not show up at first, try changing the radio button to “Show All Vulnerabilities”
  • Next, search specifically for the CVE in question:
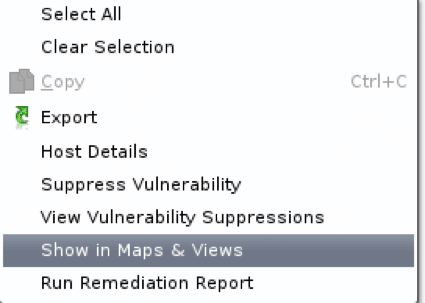
  • In the bottom details pane, you will get a list of hosts that are affected by the MOVEit vulnerability. Right click on a device and select “Show in Maps and Views”:
  • Now that you have identified which subnets these hosts live on, you can run detailed path queries from “Untrusted” to the subnet and IP in question, on TCP ports 80 and 443, to find out which firewalls are in the path and should have blocks placed on them.

Alternative Steps

An alternative method to obtain a comprehensive list of network segments is to use the Zones and Policies feature in RedSeal. Following steps 1-4 above:

  • Set up a new view in Zones and Policies and have Group A be “Untrusted”, and Group B be “Affected Hosts”.
  • Add all your Untrusted Subnets to the “Untrusted” group, and all the hosts to your “Affected Hosts” group.
  • Set up access rules between the two, such as “Approval Required”, or “Access Forbidden”, and run analysis.

Once complete, you will have a comprehensive listing of every source that can get to the specific destinations, and even run detailed path queries directly from that menu to find your firewall rules.

Share this entry

Get the latest news, invites to events, and threat alerts

Platform

  • RedSeal Platform
  • Capabilities
  • Integrations
  • CTEM

Services

  • CTEM
  • Professional Services
  • Customer Support
  • RedSeal University

Solutions

  • Business Use Cases
  • Industries
  • CTEM

Partners

  • RedSeal Partners
  • Partner Portal

Company

  • About RedSeal
  • Leadership
  • Careers

Resources

  • Blog
  • Events
  • Resource Center
CONTACT US
Distinguished Vendor badge 2025

© Copyright by RedSeal, Inc. All Rights Reserved.
  • Link to X
  • Link to LinkedIn
  • Link to Youtube
  • Link to Rss this site
  • Terms of Use
  • Privacy Policy
  • Section 508 Policy
Link to: Exploring the Implications of the New National Cyber Strategy: Insights from Security Experts Link to: Exploring the Implications of the New National Cyber Strategy: Insights from Security Experts Exploring the Implications of the New National Cyber Strategy: Insights from... Link to: The Shifting Landscape of Cybersecurity: Top Considerations for CISOs Link to: The Shifting Landscape of Cybersecurity: Top Considerations for CISOs The Shifting Landscape of Cybersecurity: Top Considerations for CISOs
Scroll to top Scroll to top Scroll to top

In order to provide you with the best experience possible we might sometimes track information about you. Sometimes this may involve writing a cookie. We use this information for things like experience enrichment, analytics and targeting advertising. We recommend allowing these functions to get the most out of your experience.

OK

Cookie and Privacy Settings


How we use cookies

We may request cookies to be set on your device. We use cookies to let us know when you visit our websites, how you interact with us, to enrich your user experience, and to customize your relationship with our website.

Click on the different category headings to find out more. You can also change some of your preferences. Note that blocking some types of cookies may impact your experience on our websites and the services we are able to offer.

Essential Website Cookies

These cookies are strictly necessary to provide you with services available through our website and to use some of its features.

Because these cookies are strictly necessary to deliver the website, refusing them will have impact how our site functions. You always can block or delete cookies by changing your browser settings and force blocking all cookies on this website. But this will always prompt you to accept/refuse cookies when revisiting our site.

We fully respect if you want to refuse cookies but to avoid asking you again and again kindly allow us to store a cookie for that. You are free to opt out any time or opt in for other cookies to get a better experience. If you refuse cookies we will remove all set cookies in our domain.

We provide you with a list of stored cookies on your computer in our domain so you can check what we stored. Due to security reasons we are not able to show or modify cookies from other domains. You can check these in your browser security settings.

Other external services

We also use different external services like Google Webfonts, Google Maps, and external Video providers. Since these providers may collect personal data like your IP address we allow you to block them here. Please be aware that this might heavily reduce the functionality and appearance of our site. Changes will take effect once you reload the page.

Google Webfont Settings:

Google Map Settings:

Google reCaptcha Settings:

Vimeo and Youtube video embeds:

Accept settingsHide notification only
NEW Gartner® Report, Emerging Tech: The Future of Exposure Management is Preemptive.Download Report.
Footer
Connect on LinkedIn