CISA AA26-097A: Iranian actors are targeting your OT Systems. Is your critical infrastructure exposed?
CISA Advisory AA26-097A is direct: Iranian-affiliated threat actors are actively targeting internet-facing programmable logic controllers (PLCs) across U.S. critical infrastructure, water, energy, and government sectors included.
The advisory describes adversaries using legitimate remote engineering tools and valid credentials to access and manipulate OT systems. That changes the fundamental security question.
It is no longer: “Are we vulnerable?”
It is: “Can an attacker reach our critical systems, and what can they do once they get there?”
What CISA’s Guidance Requires
CISA’s advisory identifies clear, actionable priorities. Organizations operating critical infrastructure must act on each:
- Eliminate unnecessary internet exposure. PLCs and OT systems should not be directly or indirectly internet-accessible. CISA specifically calls for removing inbound port exposure and ensuring all remote access is mediated through a secure gateway.
- Control and monitor all remote access. Where remote access is required, implement network proxies, firewalls, or VPNs in front of PLCs, and to enforce MFA for any access from external networks. Access should be logged, monitored, and reviewed for unusual or unexpected activity.
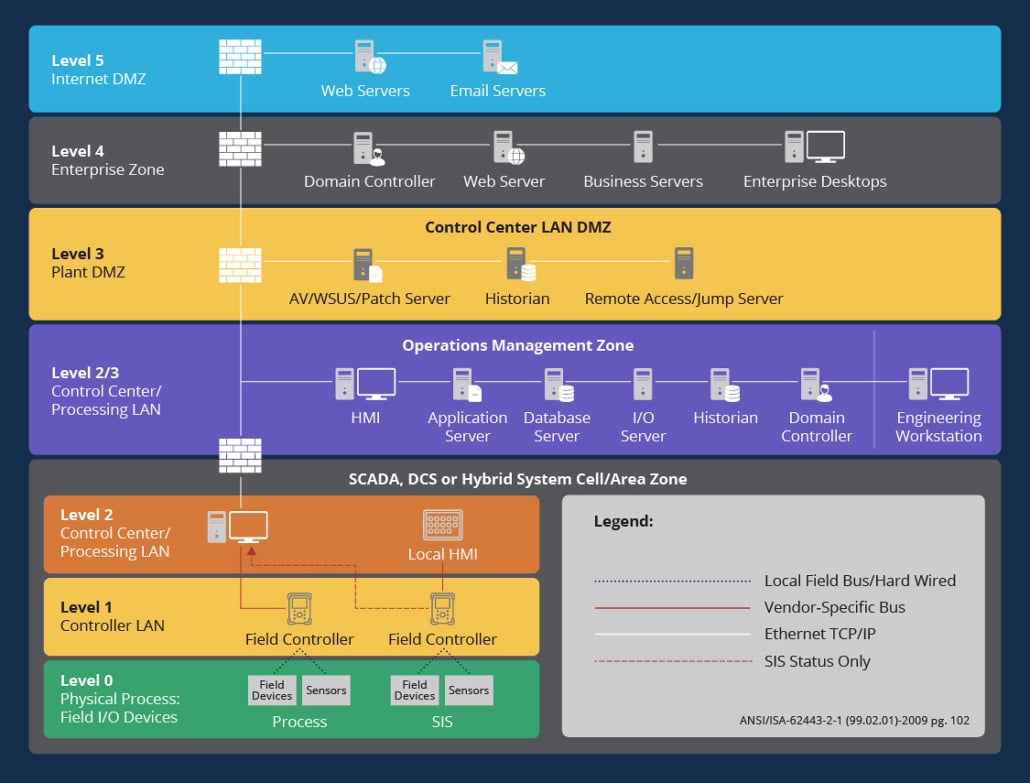
- Enforce and verify network segmentation. Configure firewalls to block unnecessary protocols by network segment, disable unused services, and implement device control lists to restrict which workstations can communicate with OT components.
- Understand attack path, not just assets. Continuously monitor network traffic for unusual logins, unexpected protocols, and ICS management commands that alter operating modes or modify programs. When adversaries use legitimate tools, behavioral context becomes the detection signal.
- Plan for operational impact. OT incidents affect operations, especially uptime and safety, not just systems. Incident response must be built for that reality.
RedSeal for IT, OT, and IoT Security
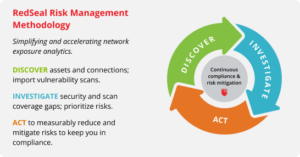
RedSeal is built for exactly this problem: understanding how a hybrid IT/OT/IoT environment is connected, what is reachable, and where exposure creates real operational risk.
- Unified hybrid visibility. RedSeal continuously models the full environment, IT, OT, IoT, and cloud, so organizations know how everything is connected.
- Attack path analysis across IT/OT boundaries. RedSeal identifies the paths an attacker could take from external entry points into OT systems, including multi-hop paths that cross network zones.
- Segmentation validation. RedSeal verifies whether controls are actually enforced, not assumed, and identifies gaps that create unintended access.
- Risk-based prioritization. RedSeal focuses remediation on exposures that create the highest operational and business risk, not simply the highest vulnerability count.
- Pre-deployment simulation. RedSeal enables teams to model the impact of network changes before implementation, reducing risk during remediation.
- Orchestrated remediation, from discovery to verified fix. RedSeal Workflow connects exposure intelligence to the tools teams already use, automating ticket creation, ownership assignment, and fix validation through a low/no-code builder driven by Agentic AI, purpose-built for exposure management.
CISA AA26-097A confirms that critical infrastructure is under active, targeted threat. The organizations best positioned to respond are those that already know:
- What is exposed
- What is reachable
- What the consequences are
RedSeal delivers a continuous visibility and understanding across the full hybrid environment, providing you the understanding you need to pre-emptively defend against active threats.
For more information on how RedSeal supports critical infrastructure security, contact us today.