Vulnerability Management Archives - Page 2 of 3 - RedSeal

Tag Archive for: Vulnerability Management

Custom Best Practice Check for Detecting Juniper Firewall Vulnerabilities

Name: Juniper Firewall Vulnerability Detection Description: This Custom Best Practice Check (CBPC) detects potential vulnerabilities in Juniper firewalls that could lead to unauthorized access and remote code execution.

Rule: Regex: ^ *web-management \{(\r?\n) *htt.*

 Explanation: This regular expression (regex) is designed to match specific configuration lines within a Juniper firewall’s configuration related to web management settings. It identifies lines that start with zero or more spaces, followed by the string “web-management {” and potentially followed by any characters related to HTTP settings.

 Purpose: Juniper firewalls are known to have vulnerabilities (CVE-2023-36844, CVE-2023-36845, CVE-2023-36846, CVE-2023-36847) that can allow unauthenticated attackers to upload arbitrary files and potentially execute remote code. This CBPC aims to identify configurations related to web management, as attackers often exploit such configurations to gain unauthorized access and control over the device. Detecting such configurations will help security teams identify potential vulnerabilities and take appropriate action.

 Instructions:

  1. Log in to the RedSeal platform.
  2. Navigate to the “Best Practices Checks” section.
  3. Create a new CBPC and give it a meaningful name and description.
  4. Copy and paste the provided regex (^ *web-management \{(\r?\n) *htt.*) into the “Rule” field.
  5. Save the CBPC and run it against the target Juniper firewall configurations.

 Outcome: When the CBPC is run against Juniper firewall configurations, it will identify any lines that match the provided regex pattern. If matches are found, it indicates potential vulnerabilities related to web management settings that might need further investigation and remediation.

***Please note that while this CBPC can help in identifying potential vulnerabilities, it’s important to have a thorough understanding of your network environment and configurations. Always perform additional assessments and validations to ensure accurate results.***

Vulnerabilities Overview:

  1. CVE-2023-36846 and CVE-2023-36847: Remote Code Execution via J-Web:These two vulnerabilities allow an unauthenticated attacker to exploit the affected Juniper firewall devices. By sending specially crafted requests to the devices, attackers can upload arbitrary files to the file system through the J-Web interface. This can lead to remote code execution and compromise the integrity and availability of the firewall and the network it protects.
  2. CVE-2023-36844 and CVE-2023-36845: Unauthorized Modification of PHP Environment Variables:These vulnerabilities enable an unauthenticated attacker to modify specific PHP environment variables on the vulnerable Juniper firewall devices. By exploiting these flaws, attackers can manipulate the behavior of the firewall’s PHP environment, potentially gaining unauthorized access and control over the device.

Potential Impact: Successful exploitation of these vulnerabilities could result in:

  • Unauthorized remote code execution, enabling attackers to compromise the firewall and the entire network.
  • Unauthorized access to the firewall’s PHP environment, leading to potential data breaches, network disruption, and unauthorized control over the device.

Additional Resources:

RedSeal will continue to monitor and test vulnerabilities, please check back for updated versions with additional refinements. Let’s discuss your concerns and how RedSeal can help, contact us today.

What the Rockwell Automation ThinServer Vulnerabilities Mean for Industrial Cybersecurity

The cybersecurity landscape is an ever-evolving domain with threats sprouting up constantly. The recent revelation concerning vulnerabilities in Rockwell Automation’s ThinManager ThinServer has highlighted the urgency for robust cybersecurity measures in the realm of industrial control systems (ICS).

Understanding the Rockwell Automation ThinServer Vulnerabilities

Rockwell Automation’s ThinManager ThinServer, a product designed for thin client and RDP server management, recently came under scrutiny after researchers from the cybersecurity firm Tenable discovered critical vulnerabilities. Classified as CVE-2023-2914, CVE-2023-2915, and CVE-2023-2917, these vulnerabilities center on improper input validation issues. They can potentially allow attackers, even without prior authentication, to induce a denial-of-service condition, delete, or upload files with system privileges.

What’s most alarming is that an attacker only needs access to the network hosting the vulnerable server for exploitation. This means that if the server is connected and exposed online – against the vendor’s best practices – it becomes susceptible to attacks directly from the internet.

The potential fallout from a successful exploitation? Complete control of the ThinServer. This presents an enormous risk, especially when considering the critical role of ICS in managing and overseeing essential industrial operations.

Enhancing Industrial Cybersecurity with RedSeal Capabilities

This backdrop brings to the fore the vital role of cybersecurity solutions like RedSeal. For existing and prospective customers, leveraging RedSeal’s capabilities can be the game-changer in fortifying their cybersecurity infrastructure.

  1. Network Visualization: RedSeal provides a detailed view of network architectures, including potential access paths. By visualizing these paths, organizations can understand how a potential attacker might navigate through their infrastructure, enabling them to take preventive measures.
  2. Risk Assessment: RedSeal’s platform assesses network risk, helping businesses identify vulnerabilities like the ones discovered in ThinManager ThinServer. By pinpointing these vulnerabilities early, proactive steps can be taken before they are exploited.
  3. Validation of Network Segmentation: Often, best practices dictate that sensitive servers, like ThinManager ThinServer, should be isolated from general network access. RedSeal can validate the effectiveness of this segmentation, ensuring that the server isn’t inadvertently exposed.
  4. Incident Response: In the unfortunate event of a breach, understanding the scope and the affected areas quickly is paramount. RedSeal’s capabilities assist in narrowing down affected segments, making response measures more targeted and effective.
  5. Continuous Monitoring: With RedSeal’s continuous monitoring, organizations can stay abreast of their network’s security posture. This ensures that as networks evolve and change, security measures evolve in tandem.
  6. Compliance Assurance: Adhering to industry standards and compliance requirements is a non-negotiable in the ICS space. RedSeal aids in ensuring that the cybersecurity measures in place align with the requisite standards, thus minimizing potential legal and reputational fallout.

In an era where cyber threats are pervasive and continuously evolving, relying on advanced cybersecurity solutions like RedSeal is no longer a luxury but a necessity. The vulnerabilities in Rockwell Automation’s ThinManager ThinServer underscore the fragility of ICS environments and the dire repercussions of lapses in cybersecurity measures. For businesses operating in the industrial domain, it’s essential to stay a step ahead. By leveraging the multifaceted capabilities of RedSeal, organizations can not only shield themselves from present vulnerabilities but also future-proof their operations against emerging threats. In the battle against cyber adversaries, being prepared and proactive is the key to victory.

The Unique Security Solution RedSeal Brings to Multi-Cloud and Hybrid Network Environments

One of the most significant benefits of implementing a multi-cloud strategy is the flexibility to use the right set of services to optimize opportunities and costs.

As public cloud service providers (CSPs) have evolved, they have started to excel in different areas. For example, programmers often prefer to use Azure because of its built-in development tools. However, they often want their apps to run in AWS to leverage the elastic cloud compute capability.

Adopting a multi-cloud strategy enables enterprises to benefit from this differentiation between providers and implement a “best of breed” model for the services that need to consume. They can also realize significant efficiencies, including cost-efficiency, by managing their cloud resources properly.

But multi-cloud solutions also bring their own challenges from administration to security. This can be especially challenging for organizations that don’t have deep experience and knowledge across all platforms and how they interconnect. It can sometimes seem like speaking a different language. For example, AWS has a term called VPC (virtual private cloud). Google Cloud Platform (GCP) uses that term, too but it means something different. In other cases, the reverse is true. The terminology is different but they do the same things.

Cloud provider solutions don’t always address the needs of hybrid multi-cloud deployments. Besides the terminology of AWS, Azure, GCP, Oracle’s OCI, IBM’s cloud, and others have different user interfaces. In a multi-cloud environment or hybrid environment, it can be far more difficult to secure than a single cloud.

Because of these challenges the need for a platform-independent solution that can understand all of the languages of each platform is needed to translate how your multi-cloud solutions are configured, interconnected, and help mitigate the risks.

How RedSeal Manages Multi-Cloud and Hybrid Cloud

At RedSeal, we provide the lingua franca (or bridge) for multi-cloud and on-premise networks. Security operations center (SOC) teams and DevOps get visibility into their entire network across vendors. RedSeal provides the roadmap for how the network looks and interconnects, so they can secure their entire IT infrastructure without having to be experts on every platform.

In most organizations using multi-cloud and hybrid cloud, however, network engineers and SOC teams are being asked to learn every cloud and on-prem resource and make sure they are all configured properly and secured. Many will deploy virtual cloud instances and use virtual firewalls, but as complexity rises, this becomes increasingly difficult to manage.

RedSeal is the only company that can monitor your connectivity across all of your platforms whether they are on-prem or in the cloud. This allows you to see network topology across all of your resources in one centralized platform.

Proactive Security

Proactive security is also complex. Most security offerings monitor in real-time to alert you when there’s an attack underway. That’s an important aspect of your security, but it also has a fundamental flaw. Once you recognize the problem, it’s already underway. It’s like calling 9-1-1 when you discover an emergency. Help is on the way, but the situation has already occurred.

Wouldn’t you like to know your security issues before an incident occurs?

RedSeal helps you identify potential security gaps in your network, so you can address them proactively. And, we can do it across your entire network.

Network Segmentation

Segmenting your network allows you to employ zero trust and application layer identity management to prevent lateral movement within your network. One of the most powerful things about RedSeal is that it provides the visibility you need to manage network segmentation.

It’s a simple concept, but it can also become incredibly complex — especially for larger companies.

If you’re a small business with 100 employees, segmentation may be easy. For example, you segment your CNC machine so employees don’t have admin rights to change configurations. In a mid-size or enterprise-level company, however, you can have an exponential number of connections and end-points. We’ve seen organizations with more than a million endpoints and connections that admins never even knew existed.

It’s only gotten more complex with distributed workforces, remote workers, hybrid work environments, and more third-party providers.

RedSeal can map it all and help you provide micro-segmentation for both east-west and north-south traffic.

Vulnerability Prioritization

Another area where RedSeal excels is by adding context to network vulnerability management. This allows you to perform true risk-based assessments and prioritization from your scanners. RedSeal calculates vulnerability risk scores that account for not only severity and asset value but also downstream risk based on the accessibility of vulnerable downstream assets.

In many cases, RedSeal uncovers downstream assets that organizations didn’t know were connected or vulnerable. These connections provided open threat surfaces, but never showed up in alert logs or only as low-to-medium risks. So, SOC teams already overwhelmed with managing critical and high-risk alerts may never get to these hidden connections. Yet, the potential damage from threat actors exploiting these connections could be even greater than what showed up as high risk.

RedSeal shows you the complete pictures and helps you prioritize vulnerabilities so you can focus on the highest risks in your unique environment.

Play at Your Best

In the late ’90s, world chess champion Garry Kasparov faced off against Deep Blue, an IBM supercomputer, in a six-game exhibition. Kasparov won the first match. Deep Blue won the second and the next three ended in draws. When Deep Blue won the final match and secured the overall victory, Kasparov was asked to concede that the best chess player in the world is now a computer.

Kasparov responded by saying that people were asking the wrong question. The question isn’t about whether the computer is better, but rather how do you play the best game of chess? Kasparov believes he lost not because the computer was better, but because he failed to perform at his best and see all of the gaps in his play.

You can’t afford to make mistakes in your security and beat yourself. By understanding your entire network infrastructure and identifying security gaps, you can take proactive measures to perform at your best.

RedSeal is the best move for a secure environment.

Learn more about how we can help protect your multi-cloud and hybrid cloud environments. Contact RedSeal today.

The Network Dimension in Vulnerability Management

By Kes Jecius, RedSeal Senior Consulting Engineer

The Center for Internet Security’s (CIS) third control for implementing a cybersecurity program is to practice continuous vulnerability management. Organizations that identify and remediate vulnerabilities on an on-going basis will significantly reduce the window of opportunity for attackers. This third control assumes you’ve implemented the first two CIS framework controls — understanding both the hardware that makes up your infrastructure and the software that runs on that infrastructure.

The first two controls are important to your vulnerability management program. When you know what hardware assets you have, you can validate that you’re scanning all of them for vulnerabilities. As you update your IT inventory, you can include new assets in the scanning cycle and remove assets that no longer need to be scanned. And, when you know what software run on your infrastructure, you can understand which assets are more important. An asset’s importance is key to identifying what should be remediated first.

Most vulnerability scanning platforms allow you to rank the importance of systems being scanned. They prioritize vulnerabilities by applying the CVSS (Common Vulnerability Scoring System) score for each vulnerability on an asset and couple it with the asset’s importance to develop a risk score.

The dimension missing from this risk scoring process is understanding if attackers can reach the asset to compromise it. Although you are remediating vulnerabilities, you can still be vulnerable to attacks if what you’re remediating isn’t accessible by an attacker. It may be protected by firewalls and other network security measures. Knowledge of the network security controls already deployed would allow the vulnerability management program to improve its prioritization efforts to focus on high value assets with exposed vulnerabilities that can be reached from an attacker’s location.

Other vulnerability scanning and risk rating platforms use threat management data to augment their vulnerability risk scoring process. While threat management data (exploits actively in use across the world) adds value, it doesn’t incorporate the network accessibility dimension into evaluating that risk.

As you work to improve your vulnerability management program, it’s best to use all the information available to focus remediation efforts. Beyond CVSS scores, the following elements can improve most programs:

  • Information from network teams on new and removed subnets (IP address spaces) to make sure that all areas of the infrastructure are being scanned.
  • Information from systems teams on which systems are most important to your organization.
  • Including network information in the risk scoring process to determine if these systems are open to compromise.

Although no single product can be the solution for implementing and managing all CIS controls, look for products that provide value in more than one area and integrate with your other security solutions. RedSeal, for example, is a foundational solution that provides significant value for meeting your vulnerability management goals by providing network context to existing vulnerability scanning information. Additionally, RedSeal provides pre-built integrations with many security products and easy integration with others via its REST API interface.

Download the RedSeal CIS Controls Solution Brief to find out more about how RedSeal can help you implement your program using the CIS Controls.

Finding Devices Vulnerable and Exposed to CVE-2018-0101 with RedSeal

Summary

Cisco has disclosed a critical CVSS 10 vulnerability in ASA that can allow an uncredentialled user to take over the vulnerable device and change access rules. RedSeal has published a custom best practice check for customers to detect vulnerable devices that have the offending service (WebVPN) enabled.

Quick Links:

What is it?

On January 29th, 2018, Cisco disclosed a critical vulnerability (CVE-2018-0101: Cisco Advisory, NVD Link) in the Cisco ASA software that runs on Cisco firewalls and other network devices. On January 30th, the advisory was updated to reflect the newly issues severity score of CVSS 10 – the highest possible score. The vulnerability is in the WebVPN feature of ASA. An uncredentialled attacker with access to the WebVPN portal can exploit the vulnerability to take over the device and execute arbitrary code, or force the device to restart.

What is the impact?

This WebVPN service is often exposed on firewalls, particularly on edge devices mediating access from untrusted networks into organization’s private networks. A successful exploit of this vulnerability can allow the attacker to take over the device, changing any routing or access rules on it to open access from untrusted networks leading to infiltration of the corporate network. Alternatively, the exploited device can be forced to restart resulting in a denial of service for anyone that depends on access which goes through the device.

Impacted Devices:

  • 3000 Series Industrial Security Appliance (ISA)
  • ASA 5500 Series Adaptive Security Appliances
  • ASA 5500-X Series Next-Generation Firewalls
  • ASA Services Module for Cisco Catalyst 6500 Series Switches and Cisco 7600 Series Routers
  • ASA 1000V Cloud Firewall
  • Adaptive Security Virtual Appliance (ASAv)
  • Firepower 2100 Series Security Appliance
  • Firepower 4110 Security Appliance
  • Firepower 9300 ASA Security Module
  • Firepower Threat Defense Software (FTD)

Mitigation and Remediation – How can RedSeal help?

Cisco is currently rolling out patches to the impacted devices. RedSeal has developed a custom best practice check and made it freely available to customers to quickly identify vulnerable devices anywhere on their network with the WebVPN service enabled. This CBPC can be manually imported into RedSeal to quickly and accurately identify which devices are vulnerable and in need of patching or other mitigation.

Being Digitally Resilient in the Face of HIDDEN COBRA

Watch Video: RedSeal and Hidden Cobra Overview, Use Cases and Demo

Introduction

On November 17th, the United States Computer Emergency Ready Team (US-CERT), in conjunction with the FBI, released a pair of advisories about the North Korean hacking and espionage campaign code named HIDDEN COBRA. The latest advisories describe two pieces of malware called Volgmer and FALLCHILL, which have been actively used to attack enterprises and other commercial entities in the US. Since 2013, organizations in the aerospace, telecommunications, and finance industries have been targeted with spear phishing campaigns.

The US-CERT advisories provide both a detailed analysis of how the underlying malware packages function as well as the detection signatures and the observed IP addresses of the command and control (C2) infrastructure. This data can be used to detect the malware on your network and sever access to its controllers (Volgmer C2 IP Addresses: CSV STIX; FALL CHILL C2 IP addresses: CSV STIX). US-CERT’s previous HIDDEN COBRA advisories from June also reveal several vulnerabilities (CVEs) that North Korean threat actors are known to target and exploit.

This article will describe how the Volgmer and FALLCHILL malware operate, what they target, how they infect those targets, the potential impacts of these infections, and effective mitigation and remediation strategies to protect your enterprise.

Summary of Suggested Actions:

  1. Identify and eliminate outbound network traffic to the C2 infrastructure.
  2. Perform a risk-based prioritization of vulnerabilities to patch on accessible and high-risk endpoints
  3. Run RedSeal’s incident response query to efficiently isolate and contain any observed indicators of compromise.

About the Volgmer and FALLCHILL Malware

Both malware packages are Windows binaries consisting of executable files and DLL counterparts able to be run as a Windows service. The primary method of attack has been through targeted spear phishing campaigns that trick victims into opening malicious attachments or clicking links leading to malicious websites exploiting browser-based vulnerabilities.

Volgmer

The Volgmer package contains four distinct modules, a “dropper”, two remote administration tools (RATs), and a botnet controller.

  • The Volgmer dropper, a Windows executable, creates a Windows registry key containing the IP address of external C2 servers. It then installs its payload (either a RAT or the botnet controller), achieving stealthy persistence by overwriting an existing Windows service DLL with the payload. Finally, it can clean up after itself and remove all traces.
  • The RAT payload, after achieving persistence on the infected Windows machine, communicates back to its C2 infrastructure over ports 8080 or 8088. The RAT enables the attacker to take over the infected computer, executing arbitrary code and exfiltrating data.
  • The botnet controller can direct the activity of other compromised computers to orchestrate DDoS attacks.

FALLCHILL

The FALLCHILL malware is a remote administration tool demonstrating a heightened degree of sophistication in its ability to remain hidden, as well as an advanced communication mechanism with its C2 infrastructure. FALLCHILL masquerades as a legitimate Windows service randomizing across seemingly innocuous service names. It generates fake TLS traffic over port 443, hiding the C2 commands and communications in the TLS packet headers, which then get routed through a network of proxy servers.
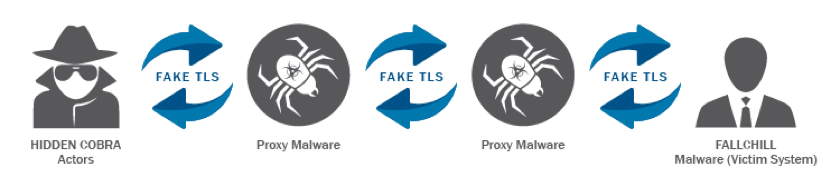
Figure 1: US-CERT visualization of how FALLCHILL communicates with HIDDEN COBRA threat actors


How the Malware Spreads and Impact of Infection

Although both malware packages are primarily distributed via targeted spear phishing campaigns, they have also been observed on malicious websites. This increases the chances for opportunistic drive-by-download infections. These targeted attacks have been seen in the US aerospace, telecommunications, and financial services.

A successful infection will result in the HIDDEN COBRA threat actors having persistent access to and control over compromised computers. The remote administration tools allow them to modify the local file system, upload files, execute files or any arbitrary code, as well as download anything on the file system. The result is that attackers will have a hidden backdoor to your system and can execute any arbitrary code. Thus, in addition to being able to exfiltrate local files such as documents directories or Outlook databases, the infection establishes a beachhead into the rest of the network from which future breaches can be staged.

General Mitigation Advice

Enterprise security organizations can take several steps to mitigate the risk of a successful spear phishing or drive-by-download infection. In the past few years, attackers have, with increasing frequency targeted end user workstations to exfiltrate local data and establish a beachhead into the rest of the corporate network. As a result, it is increasingly important to expand vulnerability management programs to include regular scans of workstations and laptops followed by timely patching of any discovered vulnerabilities. Employees, particularly executives and those exposed to sensitive or proprietary data, should be trained on practicing good email hygiene and being vigilant for possible phishing attacks. User workstations should be configured according to the principle of least privilege, avoiding local administrator level access where possible. Additionally, the US-CERT also advises limiting the applications allowed to execute on a host to an approved whitelist, to prevent malware masquerading as legitimate software.

RedSeal Can Increase Resilience and Decrease Risk

RedSeal users can decrease their risk of exposure by identifying, closing, and monitoring access from their networks to the HIDDEN COBRA C2 infrastructure. Moreover, in the event of a detected IOC, RedSeal allows you to accelerate incident investigation and containment to mitigate the impact of an infection.

1. Identify and close any existing outbound access to the C2 infrastructure

The first step is to make sure you eliminate or minimize outbound access from your networks to the HIDDEN COBRA C2 infrastructure. Since the C2 IP addresses point at proxies across the world that relay commands and data to and from the threat actors, many are associated with legitimate entities whose servers have been exploited, or commercial hosting providers whose servers have been rented. To locate access from the inside of your network to any given C2 address from the advisory, use RedSeal’s security intelligence center to perform an access query from an internal region to the internet, and in the IPs filter box, enter the IP address from the US-CERT data.
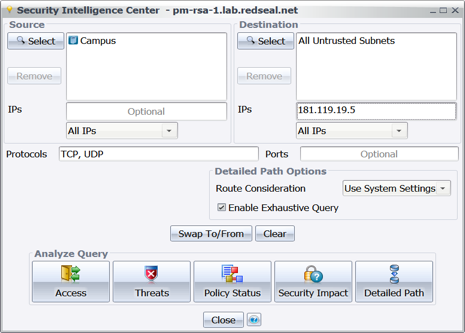
 

Figure 2: Running an Access Query from the Security Intelligence Center from internal to C2 Infrastructure
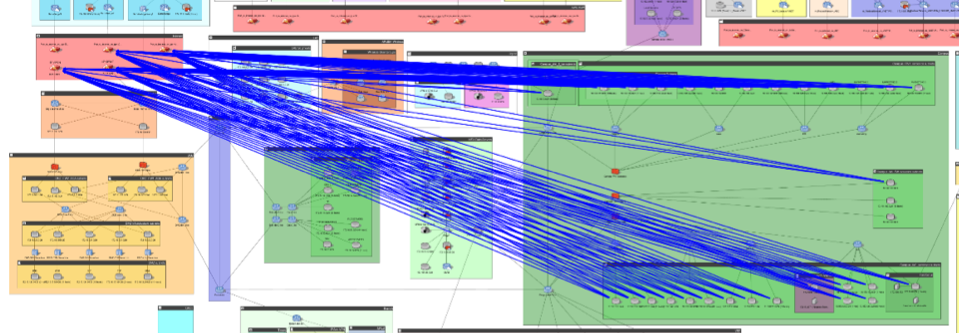
 

Figure 3: Access query results shown on map, showing existing access from internal assets to external THREAT COBRA infrastructure


With the results of the access query, the next step is to create additional controls such as firewall or routing rules to block access to the relevant IP address at your perimeter. To decide where to introduce such controls, you can run a RedSeal detailed path query to generate a visual traceroute of the offending access path(s) and identify which devices are along those paths and can be used to close access.
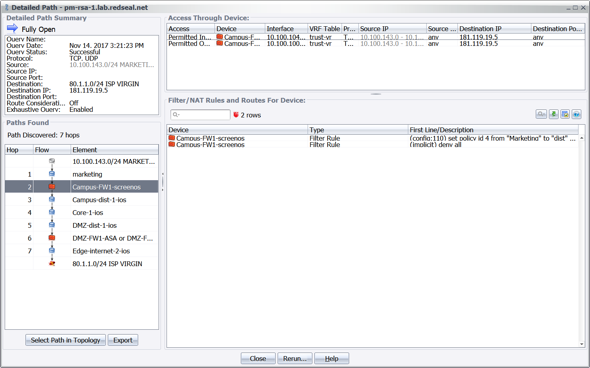
 

Figure 4: Detailed Path result identifying all network devices and relevant config locations mediating access from an internal asset to the HIDDEN COBRA infrastructure


2. Verify vulnerability scan coverage and perform a risk-based prioritization of vulnerabilities

The HIDDEN COBRA campaign has been known to use a set of five CVEs (CVE-2015-6585; CVE-2015-8651; CVE-2016-0034; CVE-2016-1019; CVE-2016-4117) as the vector for infection. These CVEs include several browser-based vulnerabilities for the Adobe Flash and Microsoft Silverlight plugins as well as a Korean word processing application. It is important to note that while these are the vulnerabilities known to be targeted in the wild to deliver Volgmer or FALLCHILL, any known or unknown Windows-based vulnerability that allows arbitrary code execution and/or privilege escalation can be used as part of a future spear phishing campaign. While it is crucial to locate and remediate the above CVEs first, it is important to perform a vulnerability scan of user workstations for all such vulnerabilities, not just the five enumerated ones.
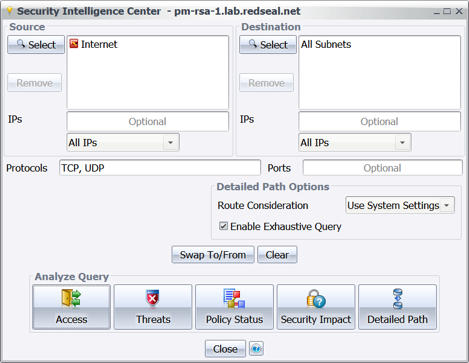
 

Figure 5: Using the Security Intelligence Center to execute a Threat Query to reveal which vulnerable assets are directly exploitable from the Internet


After importing the results of a vulnerability scan, vulnerability managers can first verify whether the scanner’s coverage was complete and identify any areas on the network missed by the scanner. This is accomplished by looking for all “Unscanned Subnets” model issues (MI-7) within your RedSeal model. A subsequent detailed path query from the scanner to the unscanned subnet will reveal whether and why access is blocked.

Next, you can perform a risk-based prioritization of the vulnerable hosts to ensure that the highest risk vulnerabilities are remediated first. The CVEs known to be actively exploited by the HIDDEN COBRA threat actors should be patched or otherwise mitigated first. A good start is to target the vulnerabilities that are on hosts that are accessible from untrusted networks, such as the Internet or a vendor’s network.

Since the malware attempts to establish a hidden Windows service with RAT capabilities, the next vulnerabilities to target for remediation are those that are directly or indirectly accessible and exploitable from any potentially compromised host. To find them, a RedSeal threat query can reveal all vulnerable hosts exploitable from a compromised endpoint on your network.
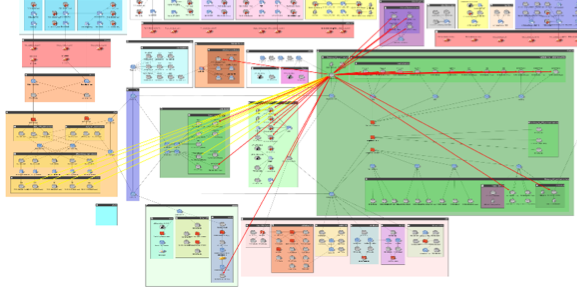
 

Figure 6: Visual results showing direct (red) and indirect (yellow) threats to the rest of the enterprise from a compromised host.
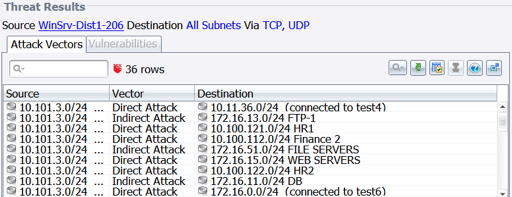
 

Figure 7: Threat Query results identifying vulnerable hosts threatened by the compromised endpoint


3. Investigate and contain existing IOCs

Finally, you can achieve greater resilience by accelerating your response to detected indicators of compromise and contain compromised systems while working to eliminate the infection. UC-CERT released several detection signatures to identify potentially compromised systems. By leveraging RedSeal’s incident response query directly or from our integrations with major SIEMs like QRadar, ArcSight, and Splunk, you can quickly assess the potential impact of a compromise and identify the mitigating controls necessary to isolate and contain it. The query allows incident responders to rapidly discover and prioritize by value all assets that are accessible from the vulnerable endpoint. A subsequent detailed path query between the vulnerable endpoint and a downstream critical asset will reveal all network devices mediating access and where controls such as firewall rules can be deployed to reduce downstream risk.
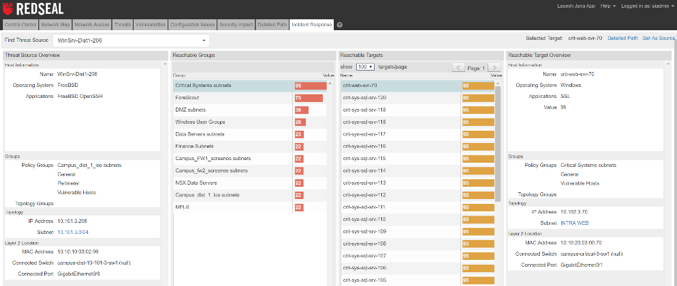
 

Figure 8: Incident Response query showing accessible groups and assets from the source of an indicator of compromise


Summary

The HIDDEN COBRA campaign is sophisticated, recently showing increases in intensity and variety of methods used. Defenders need to be resilient to minimize enterprise risk, efficiently mitigate damage, and recover from a successful compromise.  RedSeal can help you achieve resilience in the face of these changing threats — by assessing ways to block outbound access to C2 nodes, by locating vulnerable and high risk internal machines, and by speeding the investigation of any detected indicators of compromise.

____________________


Vulnerabilities: The Weeds of Your Digital Terrain

RedSeal Blog - Vulnerabilities - The Weeds of Your Digital Terrain

In the warmer months when I’m not traveling I often get up early and wander my property pulling and spraying weeds. This is an endless and thankless task, yet a necessary evil to preserve my investment and maintain appearances. I am amazed how quickly weeds grow and by the places they find purchase. In just a few days, given the right conditions whole beds can be overtaken.

A few days ago I was meandering about my yard wondering why I don’t have a gardener when it struck me. My own personal battle for yard supremacy provides a great parallel to the efforts of cybersecurity professionals. It occurred to me that vulnerabilities are the weeds of the digital terrain. They are constantly popping up in the strangest places; you can never seem to get them all; and they can quickly get out of hand if you let your attention slip.

Just like weeds, all vulnerabilities are not created equal. Their type, and more importantly their location, are factors we need to consider. The poison ivy at the far end of the property where no one goes is a concern, but far less of one than the poison ivy on the kids’ play set. In the digital terrain, this is the equivalent of vulnerabilities on assets that don’t provide access to critical data verses those that do — whether directly or via pivot attacks. So, it’s not the type of vulnerability that’s important, it’s the exposure that vulnerability delivers to critical resources that is the true cause of risk. The common practice of focusing on CAT1 vulnerabilities is inherently flawed, since the severity of the vulnerability has little to do with the risk it causes for the organization.

People have been fighting weeds since the first crops were sown sometime around 9000 BC. We know weeds and have developed many tools to fight them, yet they persist. We pull them, spray them and set up lines of defense for them to cross. Sound familiar? This is akin to patching, firewalls, and micro segmentation.

I’m making two points here: first and most importantly I need a gardener, but also it is worth reminding ourselves that vulnerabilities aren’t going away anytime soon. Regardless of how much effort you put in, you’ll never have the necessary resources to patch them all. A better strategy is to prioritize what you patch based on the actual risk it causes for your organization. A CAT1 vulnerability isolated by firewall rules provides little risk, but that CAT3 vulnerability exposed directly to the internet may provide a beachhead that exposes your most important data and systems. To quote the old adage, we need to work smarter not harder. For cyber, that means moving from a patch-based methodology to one that focuses on risk.

Digital Resilience Helps Mitigate or Prevent the ExPetr/NotPetya/ GoldenEye Malware


What is it?

The most recent malware campaign hitting Ukraine and the rest of the world is a wiper style malware which is packaged with several propagation mechanisms including the same weaponized Windows SMBv1 exploit utilized by WannaCry.  What was initially thought to be a variant of the 2016 Petya ransomware has now been shown to be a professionally developed cyber-attack masquerading as run-of-the-mill ransomware gone wild. In fact, security researchers have demonstrated that, despite demanding a ransom payment, the payload irreversibly wipes the hard drives of infected systems with no way to decrypt even if a ransom is paid to the specified wallet.

Purpose & Impact

The motivation behind the attack appears to be one of destruction and disruption. Indeed, it has had a devastating impact on enterprise’s operations world-wide as it is designed to rapidly spread throughout corporate networks, irreversibly wiping hard drive in its wake. The initial infection is believed to have targeted Ukrainian businesses and government, managing to wreak havoc in the country’s financial, manufacturing, and transportation industries. Even Chernobyl radiation monitoring systems were impacted, forcing technicians to switch to manual monitoring of radiation levels. ExPetr managed to quickly spread worldwide to thousands of computers in dozens of countries with significant disruption to major enterprises across industries as varied as shipping, pharmaceuticals, and law. Over 50% of the companies being attacked worldwide are in the industrial manufacturing or oil & gas sectors.

How it Spreads

Researchers have identified several distinct mechanisms utilized by the ExPetr malware to penetrate enterprises’ perimeter defenses for an initial infection as well as lateral movement after a successful compromise. The malware’s lifecycle is split into three distinct phases: 1) initial infection, 2) lateral movement, and finally 3) wiping the compromised system. The initial infection is believed to have spread by a malicious payload delivered through a highjacked auto-update mechanism of accounting software used by businesses in Ukraine. Alternatively, ExPetr has been observed to achieve initial infection through phishing and watering hole attacks. Next, once inside, the malware utilizes a different array of techniques to self-propagate and move laterally. Critically, ExPetr attempts to infect all accessible systems with the same Windows SMBv1 vulnerability as last month’s WannaCry attack over TCP ports 445 and 139. The malware is also able to spread laterally by deploying credential stealing packages in search of valid admin and domain credentials. It will leverage any stolen credentials to copy itself through normal Windows file transfer functionality (over TCP ports 445 and 139) and then remotely execute the copied file using the standard administrative tools, PSEXEC or WMIC.


Figure 1: Visualizing all accessible areas of the network from a compromised system.
 

How Digital Resilience Helps

Because one of the primary ways the ExPetr malware spreads is through the same Windows SMBv1 vulnerability addressed by Microsoft’s MS17-010 patch in March 2017, the same prevention and mitigation techniques described in depth in RedSeal’s WannaCry response are effective. To review:

  1. Assess and limit exposure by using an access query to discover any assets accessible through TCP ports 445 or 139 from untrusted networks like the Internet or a 3rd party.
  2. Identify vulnerable hosts and prioritize remediation efforts based on risk to the enterprise by importing vulnerability scanner findings and sorting based on risk score.
  3. Isolate critical assets and contain high risk or compromised systems by discovering and eliminating unnecessary access to or from sensitive areas of the network.
  4. Continuously monitor compliance with network segmentation policies by analyzing the relevant rules in RedSeal’s Zones & Policy.
  5. Accelerate incident response by reactively or proactively discovering the blast radius from a compromised system, understanding which assets are network-accessible and deploying the relevant mitigating controls.


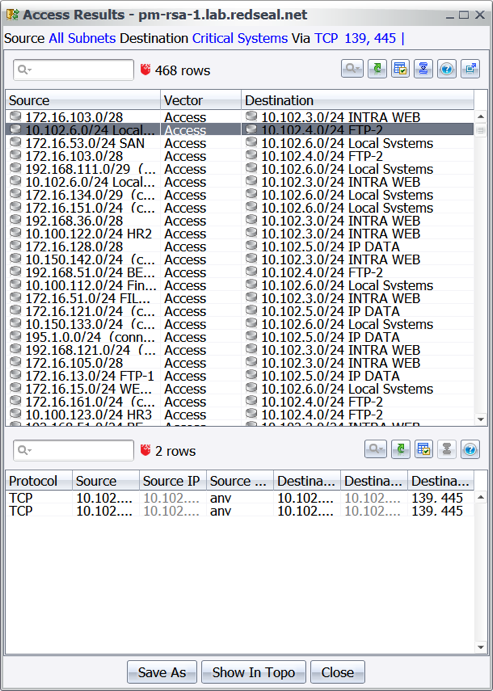
Figure 2 Results of an access query revealing what access exists from all subnets leading to the critical assets over TCP 139 or 445.
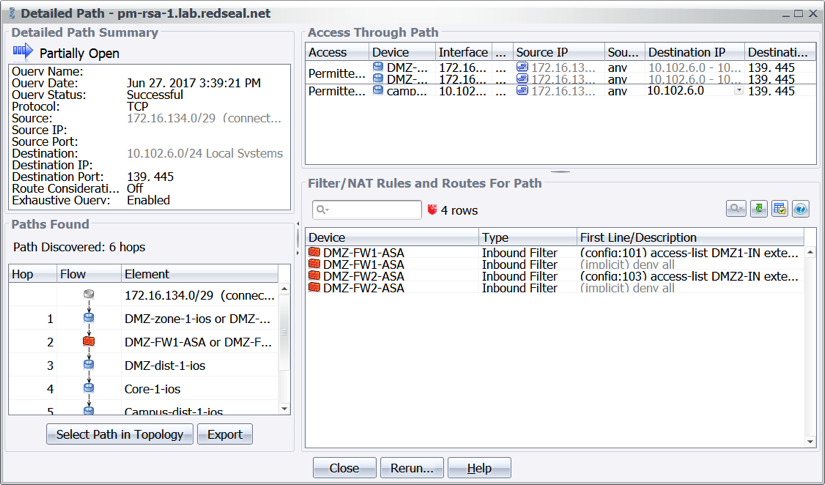

 

While applying the MS17-010 patch to vulnerable systems per a risk-based prioritization of vulnerable hosts is necessary, it is not sufficient to mitigate or prevent infection. ExPetr moves laterally through normal file-transfer and administrative capabilities using stolen credentials. As such, it is important to also reduce the attack surface of production and other mission critical assets through sensible network segmentation techniques, paying close attention to access over ports 445 and 139. RedSeal users can accomplish this by running an access query to determine what can reach critical systems through the implicated ports. Next, access that is not necessary or out of compliance can be cut off by examining the detailed path to see all network devices touched along the path and determine the optimal placement of a network countermeasure, such as a firewall rule, to eliminate the unnecessary access.


Figure 3 Detailed Path from the DMZ to a critical asset is 6 hops long with several routers and firewalls along the way


Conclusion

Cyber attacks are getting more efficient, more aggressive, and more destructive. Only a digitally resilient organization with full visibility into their network composition and security posture can hope to avoid falling victim, or to mitigate fallout in the event of compromise. Reducing your attack surface is essential to decreasing risk. This can best be done by adhering to standard IT best practices including implementing a robust backup strategy, a vulnerability management program, and a segmented internal network. In this day and age, network segmentation and micro-segmentation are increasingly important as attackers and malware routinely get past perimeter defenses, and often move laterally with impunity due to a lack of internal boundaries. RedSeal helps customers gain visibility into their network as it is built today, providing assurance through continuous monitoring of compliance with network access and segmentation policies. With the increased visibility and understanding, digitally resilient organizations can perform risk-based prioritization of remediation and mitigation activity to efficiently marshal resources and minimize overall enterprise risk.

For more information on how RedSeal can help you become resilient, please contact info@redseal.net.

NEW Gartner® Report, Emerging Tech: The Future of Exposure Management is Preemptive.Download Report.